What Is a Payload in API: 7 Essential Tips for Developers
In the world of Application Programming Interfaces (APIs), communication between different software systems is fundamental. When a client, like a web browser or a mobile app, needs to interact with a server, it sends requests and receives responses. At the heart of this exchange lies the “payload,” a crucial component that carries the actual data. Think of it as the message inside an envelope; the payload is the core information, distinct from the surrounding metadata and headers that facilitate its transmission.
An API payload is the essential data transmitted between a client and a server during an API request or response. This term’s origin stems from transportation, where “payload” refers to the cargo a vehicle carries, excluding the vehicle’s own weight. In computing, this analogy holds true, emphasizing the separation of the valuable data from the mechanisms used to transport it.
Typically, payloads are transmitted within the HTTP message body, which acts as a container for data in various formats like JSON, XML, or plain text. The Content-Type header is vital as it specifies this format, ensuring the receiving system can correctly parse and interpret the information. Different API architectures favor specific formats; RESTful APIs commonly use lightweight JSON, while older SOAP APIs rely on the more verbose XML. GraphQL, a newer query language, also uses a specialized JSON structure for its payloads. Understanding what a payload is, how it functions, and best practices for its use is essential for anyone working with APIs.
Understanding API Payload: Request vs Response
The concept of an API payload becomes clearer when we distinguish between its role in a request and a response. While both involve the transmission of data, the context and purpose differ significantly depending on whether it’s being sent from a client to a server or from a server back to a client. This distinction is fundamental to how APIs facilitate interactive and dynamic applications.
What is a payload in API request?
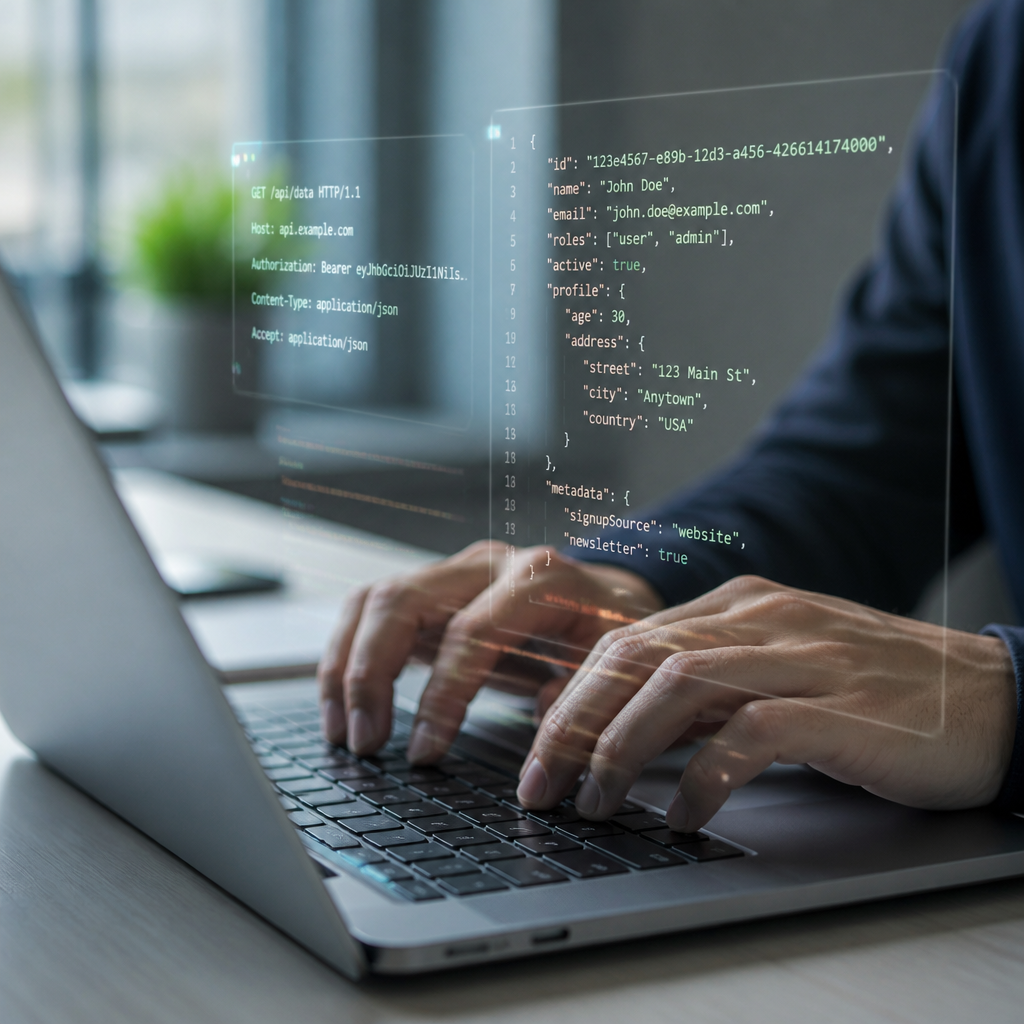
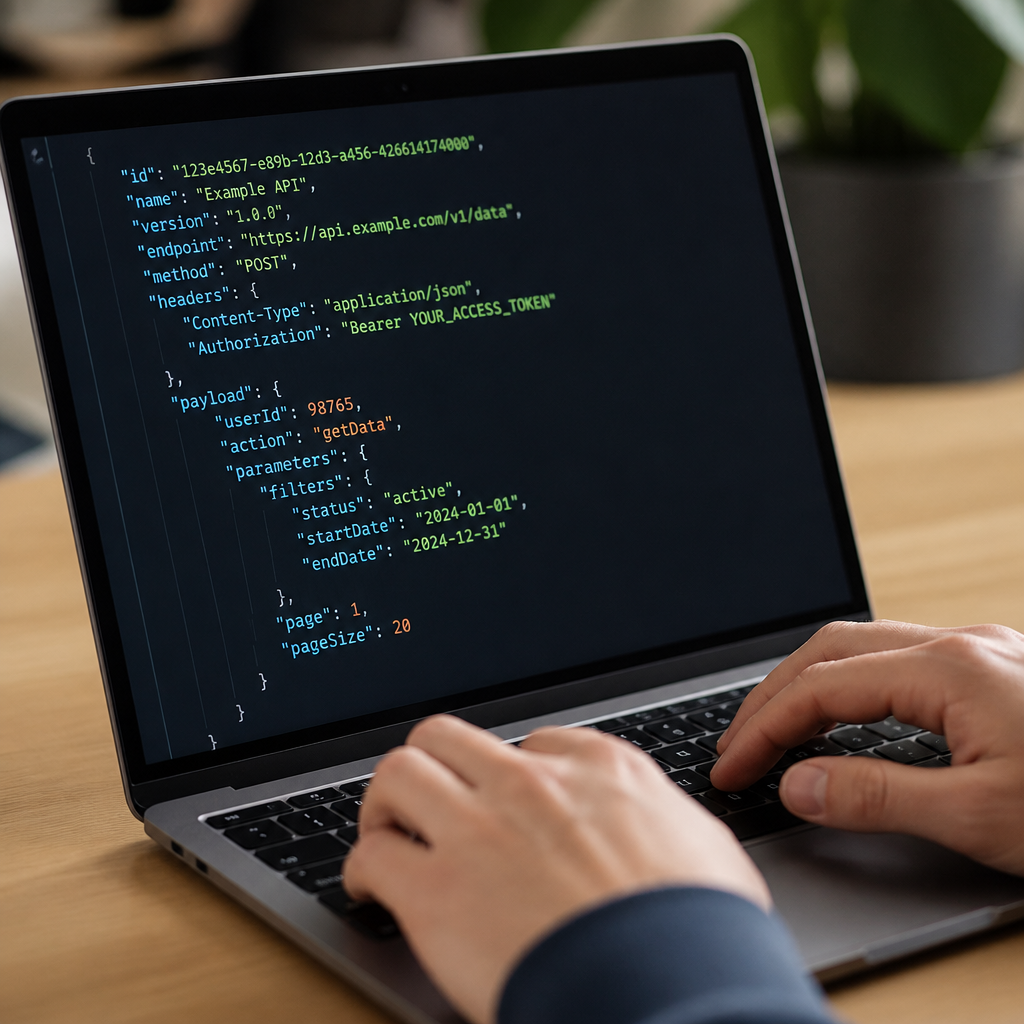
A request payload is the data sent from a client to a server when initiating an API call. Its primary purpose is to convey the information necessary for the server to perform a requested operation, such as creating a new resource or updating an existing one. The request payload is included in the body of HTTP methods designed to modify or submit data, such as POST, PUT, and PATCH.
It’s important to note that not all HTTP methods include payloads. GET requests, used to retrieve data, typically pass parameters through URL query strings. However, for creating or updating resources, POST and PUT requests are standard. A POST request might carry a payload to create a new user account, while a PATCH request would use a payload to apply partial modifications to a resource.
For example, a POST request payload for creating a new user might look like this: {"username": "john-doe", "email": "john@example.com", "age": 30}. This structured data provides all the necessary details for the server to fulfill the client’s request.
A critical aspect of request payloads is that they must strictly match the API’s expected schema, which defines the required structure and data types. _If a request payload contains invalid data—for example, an incorrectly formatted email address or a missing required field—the API will typically reject the request_ and return a 400 Bad Request error. This validation process is vital for maintaining data integrity.
What is a payload in API response?
Conversely, a response payload is the data returned by a server to a client after processing an API request. This payload contains the outcome of the requested operation, which could be the requested information, confirmation of a change, or details about an error. Every HTTP response includes a status code (e.g., 200 OK, 404 Not Found) that summarizes the outcome.
Successful responses, indicated by 2xx status codes, usually contain the requested data. For example, a successful GET request for user information might return a response payload like this: {"id": 123, "username": "john-doe", "email": "john@example.com"}. In contrast, error responses (4xx or 5xx status codes) will contain a payload explaining why the request failed, such as: {"error": "User not found", "code": 404}. This error payload clearly communicates the problem so the client application can handle it gracefully.
The size of a response payload can significantly impact API performance. Large payloads require more bandwidth and take longer to process, leading to increased latency. To optimize performance, techniques like pagination (returning data in smaller chunks) and field filtering (allowing clients to specify only the fields they need) are commonly employed.
Payload in API vs Body
In the context of APIs, the terms “payload” and “body” are frequently used interchangeably, but there is a subtle technical distinction. Understanding this difference provides deeper insight into how HTTP messages are structured. The body is the container, and the payload is the content.
| Term | Definition | Context |
|---|---|---|
| HTTP Body | The structural component of an HTTP message designed to carry data. | It is the container and can include protocol-level elements like encoding info or boundaries in multipart messages. |
| API Payload | The actual, meaningful application data that resides within the HTTP body. | It is the content and refers specifically to the core information being transmitted, like the JSON or XML data itself. |
In practice, for simple JSON or XML exchanges in most REST API interactions, the body is the payload, making the terms effectively interchangeable. The distinction becomes more relevant in lower-level protocol discussions or when dealing with complex message types like multipart/form-data, which is used for file uploads. In that scenario, the HTTP body contains multiple “parts,” each with its own headers and data, and the “payload” refers to the actual content of each individual part.
API Payload in Practice
Understanding the theoretical aspects of API payloads is crucial, but seeing them in action solidifies that knowledge. Payloads are the workhorses of API communication, enabling a wide array of functionalities across different types of applications, from creating new entries in a database to authenticating users.
Payload in API example
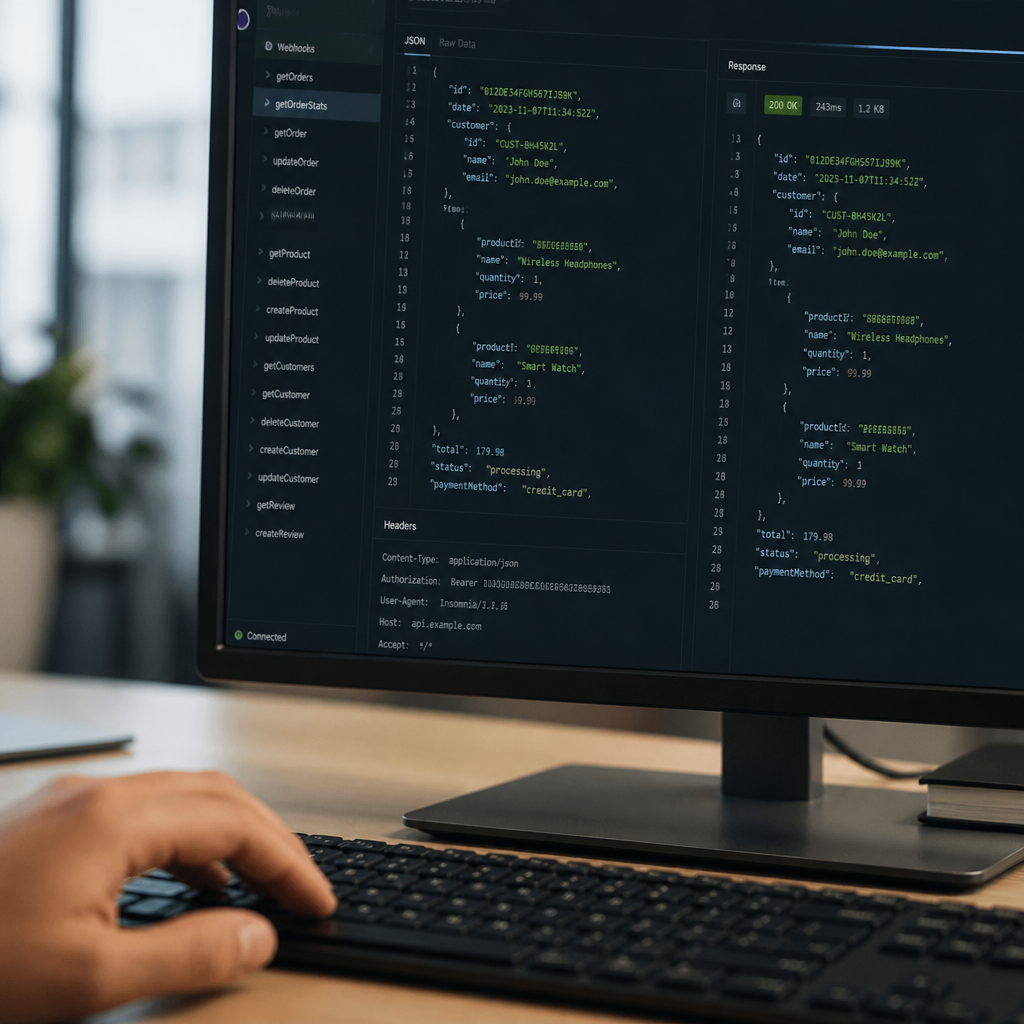
Let’s explore concrete examples of API payloads across different scenarios to illustrate their structure and purpose.
REST API Example: Creating a Blog Post
When a user creates a new blog post, the client sends a POST request to the API.
- Request Payload:
- Response Payload:
Upon successful creation, the server responds with a 201 Created status and a payload confirming the new post’s details:
Authentication Example: User Login
When a user logs in, their credentials are sent to an authentication API.
- Request Payload:
- Response Payload:
If authentication is successful, the server returns an access token that the client will use for subsequent authenticated requests.
How to send a payload in API?
Sending a payload in an API request involves several key steps, primarily determined by the HTTP method being used and the programming language or tool from which the request originates. The core idea is to package the data into the request body and set the Content-Type header to inform the server how to interpret it.
JavaScript/Fetch API Example:
In modern web development, the Fetch API is a popular choice for making HTTP requests.
Python/Requests Library Example:
Python’s requests library simplifies payload handling significantly.
When an API requires authentication, authorization tokens are typically included in the request headers. _It is a critical security practice never to include sensitive credentials like passwords directly in the payload without encryption and HTTPS_, as they could be intercepted.
Payload in API best practices
Adhering to best practices ensures that APIs are not only functional but also performant, easy to use, and resilient to potential issues. Discover the key practices for designing and implementing effective API payloads:
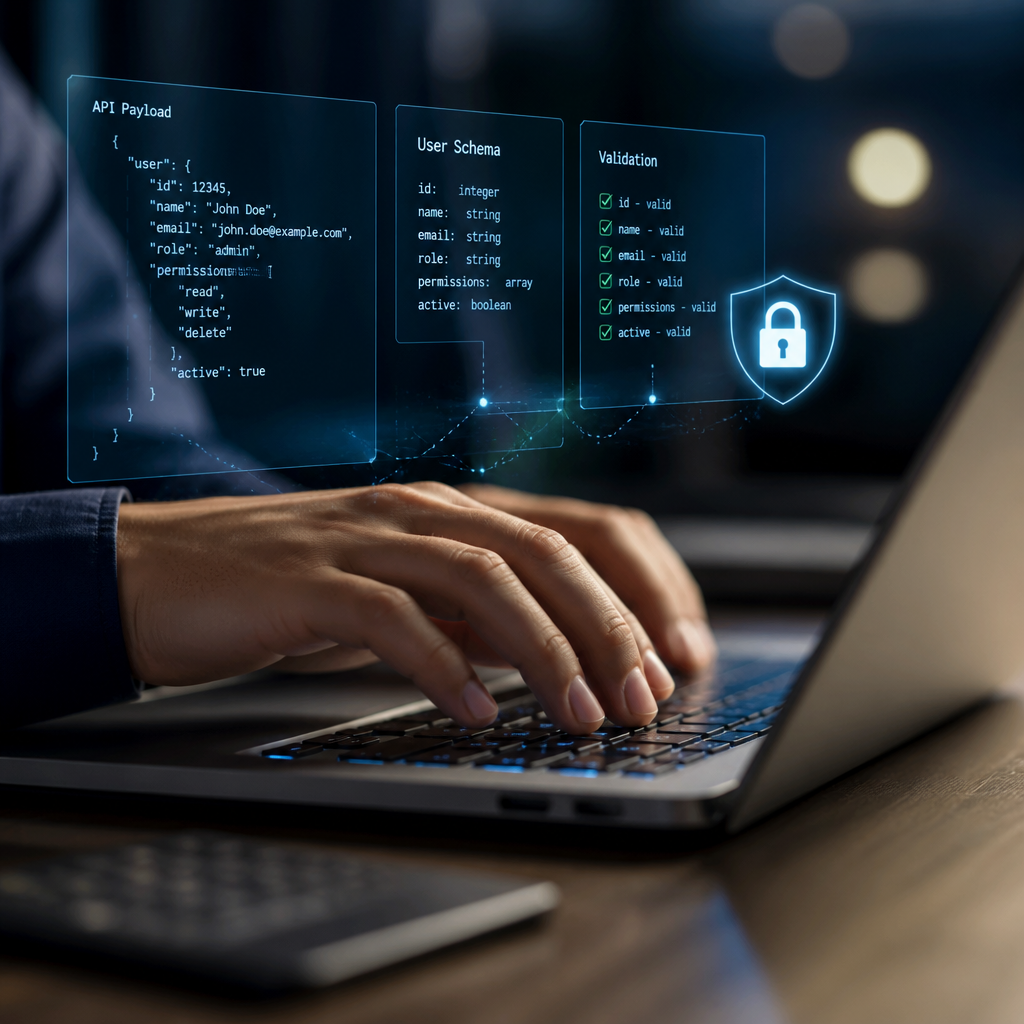
- Validation: Implement strict schema validation for all incoming payloads. If a payload does not conform to the expected structure, the API should instantly reject the request with a descriptive 400 Bad Request error.
- Size Limits: Enforce payload size limits to prevent denial-of-service (DoS) attacks. If a payload exceeds the defined limit, respond with a 413 Payload Too Large HTTP status code.
- Data Minimization: Include only the necessary data in payloads. For responses, avoid sending sensitive or irrelevant information. Techniques like field filtering allow clients to request only the fields they need, improving performance.
- Consistency: Maintain consistent naming conventions (e.g.,
snake_case), uniform date formats (ISO 8601 is a standard), and predictable structures across all payloads. Consistent design reduces the learning curve for developers. - Security: Sanitize all incoming payload data to prevent injection attacks like SQL injection. Always use parameterized queries for database operations. Encrypt sensitive data both in transit (using HTTPS/TLS) and at rest.
I’d recommend treating all incoming payload data as potentially hostile until proven otherwise.
- Idempotency: For operations that create resources (POST requests), consider using idempotency keys in the payload. This allows a server to recognize and ignore duplicate requests, enabling clients to safely retry failed requests without creating duplicate entries.
- Documentation: Thoroughly document payload schemas using tools like the OpenAPI specification. Clear documentation serves as a contract between the API provider and consumers, accelerating client development.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.