What is API Governance? 7 Benefits for Secure APIs
Imagine trying to build a sprawling digital city with every team using different instructions, unique materials, and their own architectural rules. This scenario mirrors the chaos of large software projects without a unifying strategy for how Application Programming Interfaces (APIs)—the communication pathways between software components—are managed. Without a guiding hand, data formats become inconsistent, security measures vary widely, and overall integration becomes a nightmare. This challenge highlights why a structured approach is not just a corporate buzzword; it’s essential for creating a secure, organized, and effective digital ecosystem across an entire company.
API Governance Overview
What is API Governance?
API governance is a structured and systematic approach to managing and controlling APIs throughout their entire journey, from conception to retirement. This framework includes policies, standards, and processes that ensure APIs are consistently designed, developed, deployed, and maintained across an organization. It establishes clear guidelines for decision-making, defines responsibilities, and sets up methods for enforcing rules. The main goal is to ensure all APIs align with an organization’s business goals, meet strict security requirements, and follow relevant legal and industry standards. This systematic oversight is crucial for maintaining order and efficiency in today’s increasingly API-driven world.
The scope of this discipline covers many critical aspects of API creation and operation. This includes setting clear standards for API design, establishing consistent rules for versioning to handle updates effectively, and implementing strong security measures to protect sensitive data and systems. It also defines clear rules for documentation, outlines the entire lifecycle management from creation to retirement, and details procedures for retiring older APIs. Effective implementation requires extensive teamwork, with development teams, security experts, compliance officers, and business leaders collaborating to balance innovation with risk reduction.
This structured approach is more than just a set of rules; it helps progress happen. As Kin Lane, a well-known expert in the API industry, suggests:
API governance is not just about control—it’s about enabling innovation within guardrails. Organizations that view governance as purely restrictive miss the opportunity to accelerate development through reusable patterns and standardized approaches.
This perspective highlights that this practice, when thoughtfully implemented, can make development smoother by providing clear, reusable patterns and standardized ways of working. A 2024 study published in the Journal of Systems and Software revealed that organizations implementing such frameworks experienced a 47% reduction in API-related technical debt and saw reusability rates climb from 23% to 68% over an 18-month period. In today’s regulatory landscape, this approach often becomes a legal requirement under regulations like GDPR, PSD2, and HIPAA, which mandate data protection, consent management, and detailed audit trails.
What Are the Benefits of API Governance?
Implementing a structured approach to overseeing an API ecosystem offers a wide array of strategic advantages. These benefits span across various operational areas, including enhanced security, improved consistency, stronger compliance, and greater business agility. By systematically managing their APIs, organizations can unlock significant value and reduce many risks associated with modern digital transformation.
The positive impacts are often seen across the entire software development lifecycle and influence how businesses interact with partners and customers.
- Enhanced Security: Governed APIs tend to experience 73% fewer vulnerabilities compared to their ungoverned counterparts. This reduction results from standardized security protocols, automated testing, and strong authentication mechanisms across all APIs.
- Improved Compliance and Audit Readiness: Governance frameworks provide automated documentation, change tracking, and access logs, which are invaluable for meeting the strict requirements of regulatory audits like SOC 2 and ISO 27001.
- Significant Cost Reductions: Organizations report a 30-40% reduction in development costs when existing, well-governed APIs are reused. As noted by industry experts, consolidating redundant APIs can reduce a portfolio by up to 35%, improving service quality and reducing maintenance overhead.
- Increased Developer Productivity: Productivity can see a boost of 25-35% due to self-service API catalogs, automated testing frameworks, and clear design guidelines. These resources allow developers to work more autonomously and focus on innovation.
- Greater Business Agility: Governed APIs facilitate faster partner integrations, with B2B integration times often decreasing from months to weeks. This speed allows businesses to react more quickly to market changes and launch new services.
A 2023 survey by MuleSoft of 800 IT leaders further solidified these benefits, finding that 89% of organizations with mature API programs reported improved customer experience, and 76% achieved faster digital transformation initiatives.
API Governance vs. API Management
Understanding the distinction between API Governance and API Management is crucial for any organization leveraging APIs. While both are complementary and essential, they operate at different levels. Governance represents the strategic policy-setting and oversight function, defining “what” should be done and “why.” In contrast, API Management focuses on the tactical implementation and operational control, addressing “how” APIs are deployed, secured, and monitored. _Governance without management leads to unenforced policies, while management without governance results in chaos._
The table below provides a clear comparison of the two disciplines:
| Aspect | API Governance (The ‘Why’ and ‘What’) | API Management (The ‘How’) |
|---|---|---|
| Focus | Strategic policy, standards, and compliance. | Tactical implementation, runtime control, and operations. |
| Scope | The entire API lifecycle, from design to retirement. | Primarily the deployment, runtime, and operational phases. |
| Key Activities | Defining design standards, security policies, and lifecycle processes. | Deploying gateways, enforcing rate limits, and monitoring performance. |
| Outputs | API style guides, security policies, and compliance checklists. | Gateway configurations, traffic policies, and monitoring dashboards. |
For example, a governance policy might dictate that “all APIs must use OAuth 2.0 for authentication.” The management layer then takes this policy and enforces it by configuring the API gateway to validate OAuth 2.0 tokens for every incoming request. Ultimately, organizations require both disciplines to work in tandem for a successful API strategy.
API Governance Structure and Policy
API Governance Framework
An API Governance Framework is a structured system of principles, policies, processes, roles, and tools an organization uses to manage APIs consistently. This framework acts as a blueprint, guiding all API-related activities from their inception to their eventual retirement, thereby fostering a cohesive and efficient API ecosystem. Without such a framework, organizations risk a chaotic and inconsistent API landscape, leading to increased technical debt, security vulnerabilities, and reduced reusability.
The core components typically include a defined governance structure (e.g., a central board or a Center of Excellence), a comprehensive policy framework, documented lifecycle processes, a robust tooling infrastructure, and metrics for measuring effectiveness. Key roles are also integral, including API Product Owners, Architects, Developers, and Security Champions, ensuring accountability at every level.
Lifecycle governance within the framework covers six distinct phases:
- Ideation: Approving the business case for an API.
- Design: Reviewing for compliance with established standards.
- Development: Integrating automated policy checks into workflows.
- Testing: Conducting thorough security and performance validation.
- Deployment: Requiring formal release approval.
- Operations: Involving ongoing monitoring and eventual retirement.
Policy categories are extensive, covering design standards (RESTful principles, naming conventions), security (authentication, authorization), versioning strategies, and documentation requirements. As API architect Mike Amundsen advises:
A successful API governance framework must be lightweight and developer-friendly. Heavy-handed governance creates shadow IT where teams bypass official channels. The framework should automate 80% of compliance checks and reserve human review for strategic decisions only.
_A framework should automate the majority of compliance checks, reserving human review for strategic decisions only._ Organizations often use maturity models to assess and improve their practices over time, typically implementing the framework in a phased approach starting with a pilot program.
API Governance Policy
An API Governance Policy consists of the formal rules, standards, and guidelines that dictate how APIs must be designed, developed, secured, and managed. These policies are the backbone of the governance framework, translating strategic objectives into actionable directives. Without clear and enforceable policies, the benefits of a structured approach would remain largely theoretical.
Design policies commonly mandate adherence to RESTful principles, including the proper use of HTTP verbs (GET, POST, PUT, DELETE), consistent HTTP status codes, and standardized error response formats. Security policies are paramount, often requiring robust authentication like OAuth 2.0, role-based access control (RBAC), and Transport Layer Security (TLS) for data encryption. For regulatory compliance like GDPR, policies must integrate provisions for data minimization and consent management.
Versioning policies are essential for managing API evolution, defining rules for handling breaking versus non-breaking changes and setting minimum support windows for deprecated versions. Documentation policies are critical for discoverability, often mandating machine-readable standards like OpenAPI 3.0+ and interactive documentation portals. Data governance policies address data classification, handling of Personally Identifiable Information (PII), and data retention rules.
Effective enforcement moves beyond manual reviews by integrating automated linting tools directly into CI/CD pipelines. This “shift-left” approach catches policy violations early. A 2023 study by SmartBear indicated that organizations with automated policy enforcement achieved 91% compliance rates, significantly higher than the 47% for those relying on manual reviews. A well-defined exception process is also vital, allowing for documented and time-bound waivers to ensure governance does not stifle innovation.
API Governance Implementation and Tools
API Governance Best Practices
Implementing governance effectively requires a strategic approach that fosters adoption and delivers tangible value. Adopting best practices can significantly enhance the success rate of these initiatives, ensuring APIs are compliant, efficient, and secure. Discover how these practices can transform your API ecosystem from a simple collection of endpoints into a strategic business asset.
A fundamental best practice is to start with a lightweight governance model and allow it to evolve incrementally based on feedback. Instead of launching a comprehensive rulebook, begin with 5-7 critical policies in high-impact areas like security and versioning. Automation is also key to scaling effectively. Policy enforcement should be automated by integrating tools like Spectral or Optic directly into CI/CD pipelines to catch issues early and reduce manual review overhead.
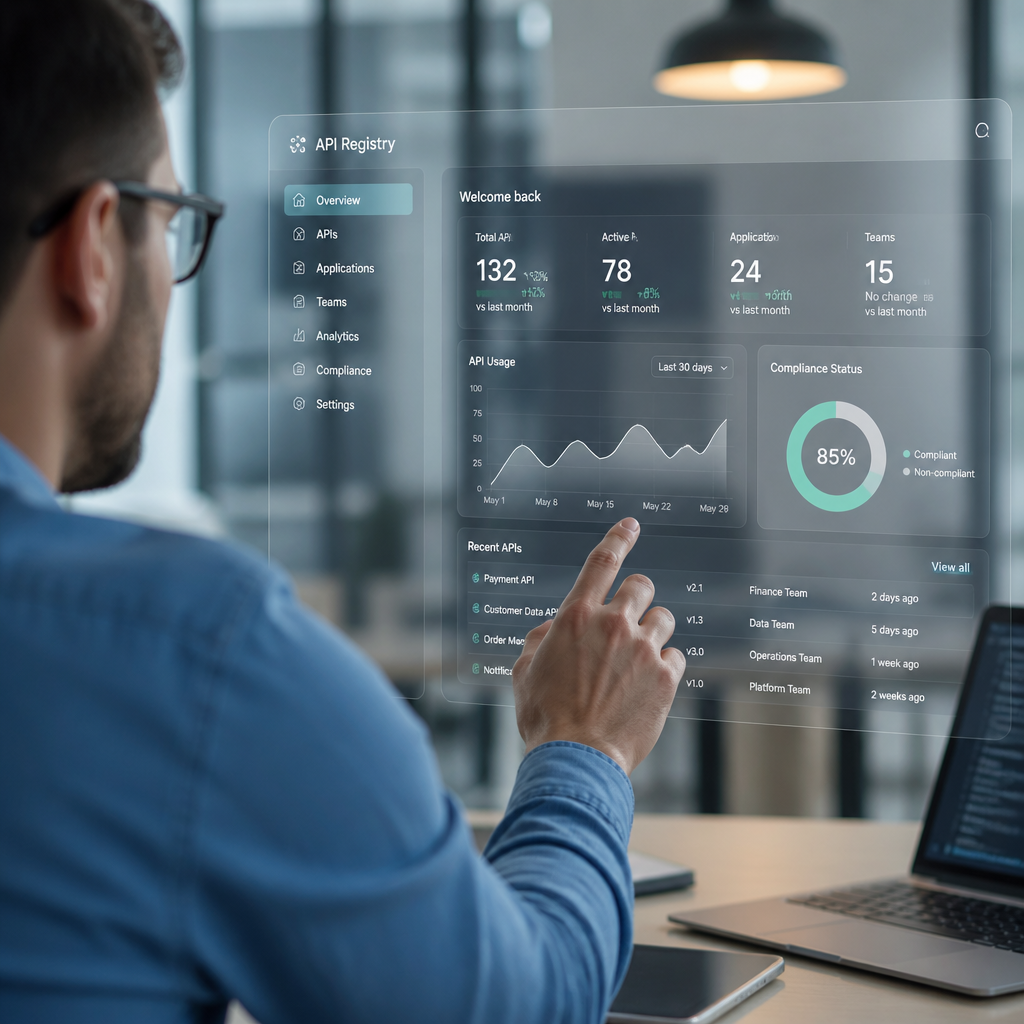
Establishing a central API catalog or registry is another critical practice, serving as a single source of truth that promotes reuse and provides visibility. A design-first approach, where API specifications are reviewed and approved before implementation, significantly reduces costly rework. To further boost productivity, create reusable design patterns and templates for common use cases like pagination and error handling.
As API strategists often advise, governance should not be a gate-keeping function but a supportive one, with champions embedded within development teams. Clear ownership models, with designated Product Owners and Architects for each API, are essential for accountability. Creating feedback loops where developers can propose policy changes ensures that rules remain practical and relevant. Finally, measuring effectiveness through key metrics—such as compliance rates, developer satisfaction, and API reuse percentages—provides objective insights for continuous improvement.
API Governance Implementation
API Governance Implementation is the practical process of establishing, deploying, and operationalizing governance frameworks and policies across an organization. _Remember that implementation is an ongoing journey, not a one-time project with a fixed end date._ A well-executed implementation can transform an organization’s API landscape from chaotic to highly efficient and secure.
The process typically unfolds in phases, starting with a current state assessment that includes creating an API inventory and conducting a maturity evaluation. A formal governance charter is then developed to establish authority, scope, and objectives, which requires executive sponsorship for organizational legitimacy and buy-in. Prioritizing policy development is crucial, focusing first on high-impact areas like security and design standards to demonstrate early value.
A pilot program with a few willing teams helps test and refine the framework before a wider rollout. Effective change management is essential to address cultural resistance, involving clear communication about the strategic benefits and developer education that shows how new processes improve quality and streamline work. Tool selection and integration are practical considerations, requiring evaluation of gateways, design tools, and catalogs based on the existing tech stack. Automation is critical for scaling, with automated policy checks integrated into CI/CD pipelines and continuous compliance monitoring dashboards. Comprehensive training, including workshops and office hours, empowers teams and fosters adoption.
API Governance Tools
Specialized software platforms and solutions are designed to automate, enforce, and monitor compliance with API governance policies throughout the entire API lifecycle. These tools are instrumental in transforming theoretical policies into practical, enforceable, and measurable actions at scale. They provide the technological backbone for maintaining a consistent, secure, and high-quality API ecosystem.
Tools fall into several key categories. API Design and Specification Tools like Stoplight Studio and SwaggerHub help create and validate API specifications against standards from the outset. API Gateway Solutions, such as Kong Enterprise and Google Apigee, are essential for enforcing security and traffic policies at runtime. API Linting and Validation Tools like Spectral and Optic automate the crucial task of checking specifications against defined rules within the CI/CD pipeline.
API Catalog and Portal Solutions, including Backstage and the Postman API Network, are vital for API discovery, promoting reuse, and providing governance visibility. API Analytics and Monitoring Tools like Moesif and Datadog play a key role in tracking compliance and performance, offering dashboards to monitor policy adherence. For more advanced needs, specialized API Security Governance Tools like 42Crunch and Salt Security offer auditing and threat detection. Open-source options like Spectral and Backstage provide powerful capabilities and lower the barrier to entry for smaller teams. A 2023 survey by Postman found that organizations using automated governance tools achieved 4.5x higher policy compliance rates compared to those relying on manual processes.
—
A mature API Governance discipline is indispensable for any organization navigating the complexities of modern digital transformation. By systematically establishing policies and processes, it ensures that APIs are built securely, consistently, and in alignment with strategic business objectives. The benefits are far-reaching, from enhancing security and compliance to boosting developer productivity and business agility. While distinct from API management, governance provides the strategic direction that management executes, making them two sides of the same coin. Implementing a robust framework, leveraging automated tools, and fostering a culture of collaboration are key to unlocking the full potential of an organization’s API ecosystem.
Frequently Asked Questions
Q1: What is the primary difference between API Governance and API Management?
A1: API Governance focuses on the strategic “what” and “why,” establishing policies and standards across the API portfolio. API Management deals with the tactical “how,” implementing gateways, handling runtime traffic, and monitoring API performance. Both are complementary but distinct.
Q2: How does API governance contribute to improved security?
A2: It significantly enhances security by mandating standardized security protocols, integrating automated security testing, and ensuring consistent authentication and authorization mechanisms across all APIs. This structured approach helps reduce vulnerabilities and protect sensitive data.
Q3: What are some key benefits an organization can expect from implementing API governance?
A3: Key benefits include reduced technical debt, improved API reusability, enhanced security, better compliance and audit readiness, reduced development costs, increased developer productivity, and greater business agility.
Q4: What are some common tools used to implement API governance?
A4: Common tools include API Design Tools (Stoplight, SwaggerHub), API Gateways (Kong, Apigee), API Linting Tools (Spectral, Optic), and API Catalogs (Backstage, Postman). Many integrate with CI/CD pipelines for automated enforcement.
Q5: Why is a “design-first” approach considered a best practice in API governance?
A5: A design-first approach is a best practice because it ensures API specifications are reviewed and approved for compliance before implementation begins. This proactive method reduces costly rework and embeds governance standards from the very start.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.