What Is Idempotent in REST API: Essential Guide
Imagine you’re trying to send an important message, but your internet connection flickers. You hit “send” again, just to be sure. What if hitting “send” multiple times actually sent multiple messages, even though you only meant to send one? This kind of problem is exactly what a crucial concept called “idempotency” solves in the world of web services, particularly in REST APIs.
When we say an operation is “idempotent” in a REST API, we mean you can send the same request to a server many times, and it will have the same final impact as if you had sent it just once. It’s like pressing a light switch: if the light is off, pressing it once turns it on. Pressing it again won’t make it more on; it just stays on. Discover why this simple idea is incredibly powerful for building reliable and trustworthy online systems.
This characteristic is vital for building robust online services, especially in distributed systems where network problems or timeouts are common. If operations weren’t safe to retry, a simple network hiccup could lead to major issues, like charging a customer twice for one purchase. The official HTTP rules clearly define this principle.
According to RFC 7231, idempotent methods are those where “the intended effect on the server of multiple identical requests with that method is the same as the effect for a single such request.”
This guarantee makes it much easier for developers to create systems that can recover gracefully from errors without causing new problems.
Idempotent HTTP Methods in REST API
Idempotent HTTP Methods Explained
In the world of the internet, HTTP (Hypertext Transfer Protocol) is the language web browsers and servers use to communicate. HTTP defines different “methods” that tell the server what we want to do. Five of these are considered idempotent: GET, PUT, DELETE, HEAD, and OPTIONS. These methods are designed so that if you send the exact same request repeatedly, the server’s information (its “state”) won’t change beyond what the very first request achieved.
Here’s a breakdown of why each one has this property:
- GET: This method is all about retrieving information. Since GET requests are only for reading data and never for changing it on the server, sending the same GET request multiple times will always give you the same information back.
- PUT: The PUT method is used to completely replace a resource at a specific address (URI). If you send the exact same PUT request multiple times, the resource will always end up in the exact same final state, containing the data from your request.
- DELETE: As the name suggests, DELETE is used to remove a resource. The first request will remove it. If you send the same request again, the item is already gone. The final state is the same: the item no longer exists.
- HEAD: This is similar to GET but only asks for the descriptive “headers” of a resource, not the content. Since it only reads information, it’s inherently safe to repeat.
- OPTIONS: This method asks the server about the communication methods available for a specific resource. It doesn’t modify any server data and is therefore idempotent.
In contrast, methods like POST and PATCH are generally considered non-idempotent. As REST creator Roy Fielding emphasized, this property is crucial for the web to function at scale, as it allows intermediary systems to safely retry failed requests without risk.
What Is the Difference Between Idempotent vs Non-Idempotent REST Methods?
The biggest difference between idempotent and non-idempotent methods is how they behave if you send them multiple times. Idempotent methods like GET, PUT, and DELETE can be safely retried without causing accidental side effects. Non-idempotent methods like POST and PATCH, however, might produce different results or create new issues each time you resend them.
Idempotent methods ensure a predictable outcome. For example, a GET request always fetches the same data, a PUT request ensures a resource matches a specific state, and a DELETE request ensures a resource is gone. Subsequent identical requests do not alter this final state.
On the other hand, non-idempotent methods can cause cumulative changes. A POST request to create an order, if sent twice, will likely create two separate orders. Similarly, a PATCH request to “add 1 to a counter” will increment the counter with each repeated request.
It’s important to understand that the response you get back from the server might be different on subsequent requests, _even if the server’s actual state remains the same_. For example, a successful DELETE might first return “200 OK,” but a second attempt might return “404 Not Found” because the resource is already gone. The key is that the resource remains deleted.
| Method | Idempotent? | Safe? | Typical Use | What Happens if Repeated? |
|---|---|---|---|---|
| GET | Yes | Yes | Retrieve data | You always get the same data back. |
| PUT | Yes | No | Replace a full resource | The resource ends up in the same final state you specified. |
| DELETE | Yes | No | Remove a resource | The resource remains deleted. |
| HEAD | Yes | Yes | Get info about data | You get the same descriptive info back. |
| OPTIONS | Yes | Yes | Ask what actions are allowed | You get the same list of allowed actions back. |
| POST | No | No | Create something new | Likely creates multiple new, separate items. |
| PATCH | No | No | Make partial changes | Changes can add up, leading to different results. |
Idempotent PUT vs POST in REST API
The choice between PUT and POST is a common design decision that hinges on idempotency and who controls the resource’s unique address (URI).
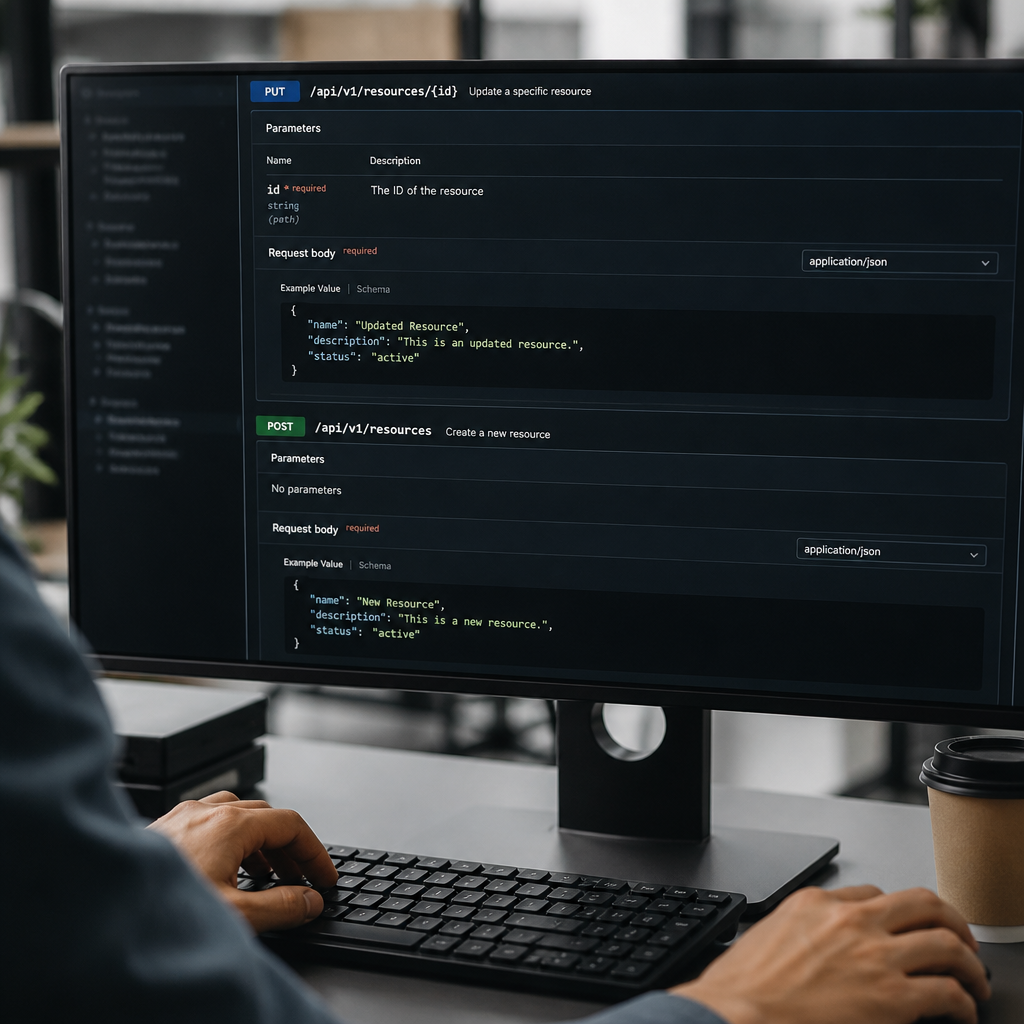
You use the idempotent PUT method when the client (your application) knows the exact URI where a resource should live. It’s like saying, “Make the resource at /users/123 look exactly like this.” If you send the same PUT request multiple times, the outcome is always the same: user 123 will have that specific data.
You use the non-idempotent POST method when you want the server to create something new and assign it a URI. It’s like saying, “Here is a new order; you decide where to put it.” Sending an identical POST request multiple times will likely create multiple distinct orders, each with its own new URI.
As HTTP expert Mark Nottingham explains, the choice often comes down to URI ownership. If the client defines the target URI, PUT is the correct choice. If the server is responsible for creating a new URI for the resource, use POST.
Idempotent DELETE Method in REST API
The DELETE method is a clear example of idempotency. Its purpose is to remove a resource, and repeating this action always results in the same final state: the resource is no longer there.
The first DELETE request for a resource will remove it, and subsequent identical requests will find it already gone. While the server’s state remains consistently “deleted,” the HTTP response code might change. The first successful DELETE might return a 200 OK or 204 No Content. A subsequent attempt for the same resource, which no longer exists, will likely return a 404 Not Found.
This behavior is correct and expected. Even in systems using “soft deletes” (where an item is marked as deleted instead of being physically removed), the operation remains idempotent. Sending multiple DELETE requests simply ensures the item stays marked as deleted.
Idempotency in REST API Design and Practice
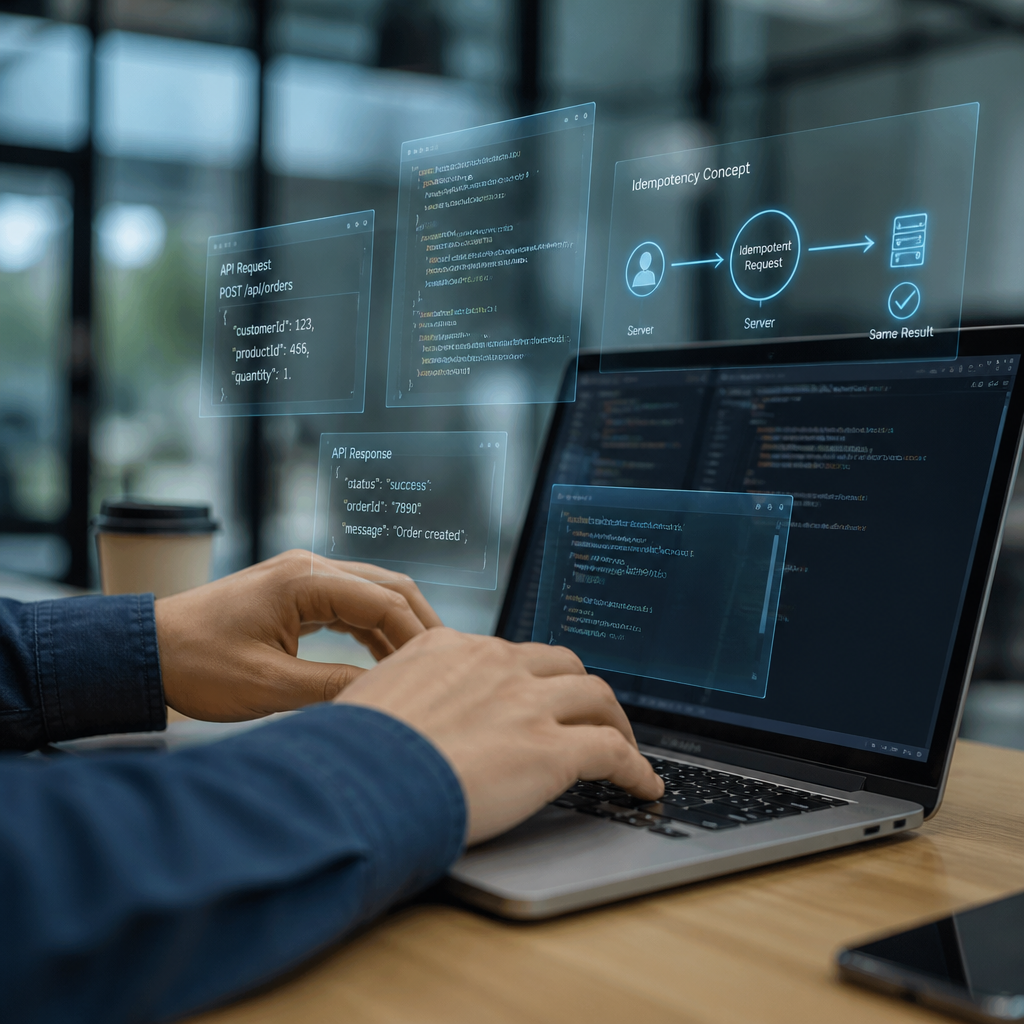
Why Idempotency Matters in REST API Design
Idempotency is a cornerstone of reliable and robust API design. It solves fundamental challenges that arise when systems communicate over unreliable networks.
- Enables Safe Request Retries: Networks fail. When an application sends a request and doesn’t get a response, it can’t be sure if the request was processed. With idempotent operations, you can retry with confidence, knowing the server will end up in the desired state. It is a critical feature for handling network timeouts and transient errors, as _retrying that request is risky without idempotency_.
- Enhances System Reliability: In a payment system, a non-idempotent charge request could lead to double-billing if retried after a network glitch. Idempotency prevents these critical errors, making the entire system more resilient.
- Prevents Duplicate Operations: This principle prevents creating duplicate user accounts, sending the same notification multiple times, or adding duplicate items to an inventory. It ensures that an action’s effect on system data happens only once.
- Simplifies Client-Side Logic: Without idempotency, client applications need complex logic to track every request’s status before retrying. With it, clients can use simple retry strategies without worrying about causing duplicate actions.
- Supports Scaling and Load Balancing: In large systems, load balancers can safely retry a request on a different server if the first one fails, which improves efficiency and robustness.
As microservices expert Sam Newman emphasizes, the ability to safely retry operations is essential for microservices to communicate effectively and for the overall system to remain resilient, even when parts of it temporarily fail.
Idempotent Operations Real World Examples
Idempotency is a practical concept used by many online services every day. For example, in e-commerce payment processing, companies like Stripe master this principle. To prevent double-billing, services like Stripe use an “Idempotency-Key” (a unique ID generated by your application) in the request header. If the same key is sent again, Stripe recognizes it and returns the result of the original charge, ensuring the customer is charged only once.
Other examples include banking transfers, where a unique transaction ID in a PUT request ensures a transfer only occurs once, and user profile updates, where a PUT to a specific user ID consistently sets their profile data. Cloud services like AWS S3 handle file deletions idempotently, and content management systems use PUT to update specific posts without creating duplicates.
| Service | Operation | Method | How Idempotency is Achieved | Business Impact |
|---|---|---|---|---|
| Stripe | Create charge | POST | Uses an “Idempotency-Key” header. | Prevents customers from being charged multiple times. |
| PayPal | Process payment | POST | Uses a client-generated transaction ID. | Ensures a single payment transaction occurs. |
| AWS S3 | Delete object | DELETE | Relies on the inherent nature of DELETE. | Allows safe retries when deleting cloud storage files. |
| Shopify | Update product | PUT | Replaces the entire resource at a known ID. | Guarantees consistent product information. |
| Twilio | Send message | POST | Uses an idempotency key. | Prevents sending the same message multiple times. |
In essence, idempotency is a vital foundation for building robust and user-friendly online services. By designing operations with this principle in mind, developers create systems that gracefully handle network uncertainties, leading to more predictable behavior and a better user experience.
FAQ
Q1. What does “idempotent” mean in the context of REST APIs?
A1. In REST APIs, an idempotent operation is one where making multiple identical requests produces the same result on the server as making a single request, without causing any additional side effects or changes to the server’s state beyond the initial action.
Q2. Which HTTP methods are considered idempotent?
A2. The HTTP methods considered idempotent are GET, PUT, DELETE, HEAD, and OPTIONS. These methods are designed so that repeating them multiple times will not change the server’s state beyond what the first request accomplished.
Q3. How does PUT differ from POST in terms of idempotency?
A3. PUT is an idempotent method used to create or replace a resource at a specific, client-known URI. POST is a non-idempotent method typically used to create new resources where the server assigns the URI. Repeated PUT requests to the same URI will result in the same final resource state, while repeated POST requests will likely create multiple distinct resources.
Q4. Can the response code for an idempotent operation change on subsequent requests?
A4. Yes, the HTTP response code for an idempotent operation can change on subsequent requests, even if the server state remains the same. For example, a DELETE request might return 200 OK on the first successful deletion, but 404 Not Found on subsequent attempts for the same, now non-existent, resource. The key is that the resource’s state on the server is consistently “deleted.”
Q5. Why is idempotency important for REST API design in real-world applications?
A5. Idempotency is crucial for REST API design because it enables safe request retries, which is vital in distributed systems prone to network failures and timeouts. It helps prevent duplicate operations (like double-charging in payment systems), improves system reliability, and simplifies client-side implementation.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.