What Is API Authentication: 5 Secure Methods Explained
Have you ever logged into your banking app, ordered food online, or refreshed a social media feed? When you do, you’re interacting with something called an Application Programming Interface, or API. Think of it as a digital waiter that takes your order from the app (the “client”) and delivers it to the server (the “kitchen”) holding all the data. I remember the wonder I felt when first learning to code, seeing two different software systems “talk” using an API – it was a powerful concept. But just as you wouldn’t let just anyone into a restaurant’s kitchen, APIs require strong security. That’s where API authentication comes in: it’s a critical security step that verifies your identity, ensuring only legitimate users or applications can access sensitive data and perform actions through these digital gateways.
In our interconnected world, the importance of robust API authentication can’t be stressed enough. I’ve seen firsthand how quickly things can unravel with weak authentication. It’s like leaving your front door unlocked; a poorly secured API leaves your data vulnerable. Data breaches are unfortunately common, often stemming from inadequately guarded digital gateways. A striking 94% of organizations experienced API security incidents in 2023, with authentication vulnerabilities being a major contributing factor (4). This isn’t merely a technicality; it has significant financial and trust implications. The API management market’s rapid expansion, projected to reach $25.8 billion by 2030, signals that businesses are increasingly recognizing this critical need and investing in better authentication (5).
Understanding the difference between _authentication_ and _authorization_ is fundamental for anyone building or securing APIs. Mark O’Neill, VP of Innovation at Axway, aptly describes API authentication:
“the first line of defense” (6).
It answers the question, “Who are you?” Is your claimed identity genuine? _Authorization_, conversely, follows authentication and answers, “What are you allowed to do?” Being authenticated doesn’t grant unlimited access. You might be authenticated to view your bank balance, but you won’t be permitted to transfer funds from someone else’s account. This distinction, which I learned the hard way while troubleshooting access issues on a client project, is paramount for building truly secure systems (3).
How Does API Authentication Work?
How Exactly Does API Authentication Work?
API authentication functions much like a secret handshake. When your app (the “client”) needs to communicate with an API server, it first sends a request containing some form of identification. This could be a password, a special code, or a digital “token.” The API server then acts like a bouncer, verifying these credentials against its records. If they match, the server grants access to the requested information or service. Otherwise, access is denied (8, 9). This verification process ensures that every interaction with the API is legitimate, keeping your data secure.
The typical process begins with you (the client) presenting your credentials, which might be a username and password or an API key—think of it as a unique digital ID card. The API server then rigorously checks these credentials. If they are valid, instead of asking for your full ID repeatedly, the server issues a temporary “access badge,” known as an authentication token. For all subsequent requests, you simply present this badge, and the server quickly verifies it, allowing you through without needing to re-check your entire identity each time (10). This token-based approach proves incredibly efficient for applications making numerous API calls.
A significant trend in modern API design involves adopting “stateless” authentication, particularly with technologies like JSON Web Tokens (JWTs). This means the server doesn’t need to maintain session information for every client. Instead, all necessary identity verification is contained within the token itself. This approach is transformative for large, distributed systems, as it reduces server load and simplifies scaling. When an API call is made, authentication credentials are typically placed in a specific part of the request, such as the Authorization header in an HTTP message. The server validates these credentials and, if approved, issues the authentication token for future use (11, 12, 13).
During my internship, I was tasked with implementing OAuth 2.0 authentication for a new client-facing API. I quickly realized that sending credentials over the internet without proper protection is akin to shouting your password in a crowded room. This is why securing the initial “handshake” is so important. We implemented HTTPS/TLS encryption, which encapsulates all communications within a secure, encrypted tunnel, shielding sensitive data from eavesdroppers and tampering (14). It was a challenging learning curve, and I recall spending nearly two weeks configuring the OAuth 2.0 flow correctly, whereas a simpler API key implementation might have taken only a few hours. This experience highlighted the trade-offs between security, complexity, and development time, a point also underscored by Postman’s survey (15).
What Exactly Is an API Authentication Token?
An API authentication token acts as a digital pass, confirming your identity when accessing an API. After you’ve successfully presented your initial credentials to the authentication server, it issues this token. Subsequently, instead of showing your full identification for every interaction, you present this token with each API request. It’s similar to checking into a hotel: you show your passport once, receive a key card, and then use that card to access your room and other hotel facilities (17, 18). These tokens are central to building fast, secure, and scalable APIs today.
Most tokens, especially the widely used JSON Web Tokens (JWTs), feature a distinct three-part structure separated by periods. The first part, the “header,” specifies the token type and the cryptographic algorithm used for its security. The second part, the “payload,” contains important claims or information about you, such as your user ID, role, or token issuance time. The final part, the “signature,” functions as a tamper-proof seal. It’s a unique cryptographic hash generated from the header and payload using a secret key, which is crucial for the API server to verify that the token has not been altered since its issuance (19). The self-contained nature of JWTs offers a significant advantage, particularly in microservices architectures.
A vital security feature of these tokens is their “lifespan” or expiration time, a deliberate measure to mitigate risks if a token is compromised. “Access tokens,” used for direct API interactions, typically have a short duration, often 15 to 60 minutes. This limits the window for a malicious actor to exploit a stolen token. To prevent users from having to log in hourly, “refresh tokens” are often used in conjunction. These refresh tokens have a much longer lifespan—days or even months—and are solely used to securely obtain new access tokens when the current one expires (20, 21). This dual-token strategy effectively balances strong security with a seamless user experience.
The most common type of authentication token you’ll encounter is a “Bearer” token. When you see “Authorization: Bearer <token>” in an HTTP request header, that’s what’s being used (22). The term “Bearer” signifies that whoever possesses the token is granted access. _Consequently, keeping these tokens confidential is paramount!_ Tokens can also be “opaque,” meaning they are simply random strings providing no inherent information; the server must look them up. “Self-contained” tokens, like JWTs, differ because they carry all necessary information (in the payload) and are cryptographically signed, enabling the server to validate them without a database lookup (24). Self-contained tokens generally simplify the process for the API server.
When I was troubleshooting an XSS vulnerability a few years ago, I deeply understood why token storage on the client-side is so critical. Storing tokens in a browser’s localStorage, for instance, is often considered risky because a malicious script could potentially steal them. Using httpOnly cookies provides better protection against XSS because JavaScript cannot directly access them. However, httpOnly cookies can be vulnerable to Cross-Site Request Forgery (CSRF) attacks if additional security measures, like CSRF tokens, aren’t implemented (25). It’s a continuous balancing act, and the optimal approach depends heavily on the application type and data sensitivity.
API Authentication Methods and Types
Types of API Authentication
API authentication types represent the various established strategies used to confirm the identity of a client attempting to connect with an API. Each type offers distinct advantages and disadvantages concerning security levels, setup complexity, and suitability for specific scenarios (26, 27). For example, selecting a method for a public weather API differs significantly from choosing one for a highly secure financial transaction API. Understanding these differences is crucial for developers and organizations to select the appropriate security measures, balancing robust security with usability.
Let’s examine some common types of API authentication. Basic Authentication is straightforward: you encode a username and password in Base64 and transmit it. While easy to implement, it’s quite insecure unless always used over HTTPS. API Keys are unique strings assigned to clients, functioning like a secret password for your application. They offer moderate security and are convenient for server-to-server communication. OAuth 2.0 is a prominent framework that allows third-party applications to access your resources without direct access to your password. JSON Web Tokens (JWTs) are self-contained tokens providing high security with moderate complexity. SAML is primarily used for enterprise “Single Sign-On” (SSO). Lastly, Mutual TLS (mTLS) offers the highest level of security, where both the client and server authenticate each other using digital certificates (28).
Developer surveys reveal clear community preferences. RapidAPI’s 2024 Developer Survey indicated that OAuth 2.0 is the most widely adopted, used by 41% of developers, with API Keys following at 28%. This trend reflects a growing acknowledgment of the necessity for more robust, token-based identity verification in modern APIs (29). The flexibility and security of OAuth 2.0, despite its complexity, make it indispensable for public-facing applications.
Different situations call for specific strategies, and making the right choice can prevent future complications. For instance, if you have a trusted backend service communicating with another internal service, an API Key might suffice. However, for applications where users log in via a third party (like “Log in with Google”), OAuth 2.0 is the appropriate choice. In microservices environments, JWTs are advantageous due to their stateless nature. For applications with the most stringent security requirements, such as critical financial systems, mTLS provides unparalleled mutual trust (31).
Regulatory requirements often heavily influence choices. For example, handling credit card data necessitates adherence to the PCI DSS 4.0 standard, which prohibits Basic Authentication over unencrypted connections and mandates multi-factor authentication (MFA) for accessing cardholder data (32). These are not mere suggestions but strict rules with potentially severe penalties for non-compliance. This underscores that API security extends beyond coding practices to encompass legal and ethical obligations.
API Authentication Methods
While “types” represent broad strategies, specific “methods” refer to the technical implementations of these strategies. These methods detail how credentials are exchanged, how tokens are generated and validated, and how sessions are managed during client-server interactions (33, 34). It’s comparable to distinguishing between the general concept of “transportation” (the type) and the specific mechanics of a car or bicycle (the methods).
Many methods are based on standardized blueprints known as HTTP Authentication Schemes, defined in RFCs by the Internet Engineering Task Force. For instance, RFC 7235 outlines HTTP principles and covers schemes like Basic and Digest authentication. Crucially for modern APIs, RFC 6750 defines Bearer tokens, which are fundamental to OAuth 2.0 and JWT verification (35, 22). These RFCs serve as instruction manuals, ensuring compatible and secure system development.
API Key authentication is among the simplest methods. You generate a unique string for your client, which serves as the API key. When your app makes a request, it includes this key, typically in an HTTP header (like X-API-Key). The API server then checks this key against its list of valid, active keys. Access is granted if the key is recognized; otherwise, it’s denied (36).
OAuth 2.0 is a framework comprising several specific “grant types” or “flows.” The Authorization Code grant type is common for standard web applications. The Client Credentials grant type is ideal for machine-to-machine communication. The Resource Owner Password Credentials grant type enables trusted applications to use a user’s username and password directly. _This grant type should be used with extreme caution as it directly exposes user credentials to the client application_ (37).
JWT (JSON Web Token) authentication utilizes the three-part tokens—header, payload, and signature. The key aspect lies in the cryptographic signature, created using algorithms like HMAC or RSA. This signature allows the server to verify that the token hasn’t been tampered with. A major advantage of JWTs is their “statelessness”: the server doesn’t need to query a database for session information to validate them, making them highly efficient (38).
Mutual TLS (mTLS) authentication involves both the client and server presenting digital certificates to each other. If both certificates are valid and issued by trusted authorities, a secure, mutually verified connection is established (40). This method offers extremely high security and is typically employed in highly regulated enterprise environments.
Philippe De Ryck, a respected web security expert, offers invaluable advice:
“The choice of authentication method should be driven by your threat model, not by implementation convenience” (41).
This means avoiding the easiest option and instead considering what you’re protecting and from whom. While API keys are simple, they function like long-lived passwords. For sensitive data, OAuth 2.0, with its short-lived, rotating tokens, represents a superior security choice.
Another clever method is HMAC (Hash-based Message Authentication Code) authentication. In this method, both the client and server share a secret key. The client generates a unique “hash” of the request’s content using this secret key and sends it along. The server independently computes its own hash of the received request. If the two hashes match, the server confirms that the request is authentic and has not been altered (42).
API Authentication vs Authorization
Understanding the distinction between identity verification and authorization is critical for anyone involved in API security. These are separate, sequential steps. API authentication is about proving who you are. It’s the process of verifying your identity as a user, application, or service (43, 44). Consider it like showing your ID at the entrance of a building.
Once your identity is successfully verified, the system proceeds to authorization. This step determines what you are allowed to do or what resources you can access. It answers the question, “What can you do?” (43, 44). So, after showing your ID, authorization is like receiving a pass that grants access to the first floor but not the restricted data center on the fifth floor.
Crucially, authentication always precedes authorization (45). You must first prove your identity before the system can assess your permissions. If identity verification fails, authorization checks become irrelevant.
The table below summarizes the key differences:
| Feature | Authentication | Authorization |
|---|---|---|
| Purpose | Verifies identity (“Who are you?”) | Grants permissions (“What can you do?”) |
| Process | Uses credentials, tokens, or biometrics | Uses roles, scopes, or policies |
| Timing | Occurs once per session or transaction | Occurs with every resource access request |
| Outcome | Identity confirmed, session initiated | Access granted or denied to a resource |
Let’s consider a real-world example using OAuth 2.0. When linking a new fitness app to a Google account, the initial step is authentication: Google verifies your identity. Once authenticated, Google asks you to grant specific permissions (called “scopes”) to the fitness app, such as “read my activity data.” This act of granting permissions is the authorization step (47).
Authorization frameworks can be sophisticated. For instance, Attribute-Based Access Control (ABAC) offers a dynamic approach. Instead of relying on roles, it uses a combination of attributes—such as the user’s identity, the resource being accessed, the action attempted, and environmental factors like the time of day (48).
One of the most dangerous vulnerabilities arises from conflating these two concepts. This occurs when developers assume that authenticated users have unrestricted access. Such mistakes can lead to severe “privilege escalation” attacks. To prevent this, every API request must undergo a meticulous authorization check, ensuring that even authenticated users operate strictly within their defined boundaries (50).
API Authentication Best Practices and Troubleshooting
API Authentication Best Practices
API authentication best practices are the foundational guidelines for securing your APIs. These industry-recommended principles are designed to close security gaps, defend against common attacks, and ensure only verified identities interact with your systems (51, 52). Adhering to these practices is often a mandatory requirement for regulatory compliance and for maintaining user trust. The fact that “Broken Authentication” ranks as the second most critical API security risk according to OWASP highlights its importance (53).
First and foremost, always use HTTPS/TLS encryption for all API communications. This is non-negotiable. Without HTTPS, any credentials or tokens transmitted between your app and the API server are exposed in plain text, making them susceptible to interception (54).
OWASP, a key resource for web security, provides a comprehensive list of best practices, including (59):
- Using HTTPS exclusively for all communication.
- Implementing token expiration with refresh mechanisms.
- Enforcing rate limiting to prevent brute-force attacks.
- Using strong, salted password hashing algorithms (e.g., bcrypt, Argon2).
- Validating tokens on every single request.
- Implementing multi-factor authentication (MFA) for sensitive operations.
- Logging all authentication events for auditing and monitoring.
- Ensuring secure token storage on the client-side.
Another critical practice is implementing token expiration and refresh mechanisms. Access tokens should have a short lifespan, ideally expiring within 15–60 minutes. This limits the damage if a token is compromised. To maintain a smooth user experience, pair these with longer-lived refresh tokens used to securely obtain new access tokens (55).
To thwart brute force attacks, you must implement rate limiting and throttling. This restricts the number of login attempts allowed within a specific timeframe. NIST suggests limiting failed attempts to around 10 per account within five minutes (56).
When it comes to passwords, employ strong, one-way hashing algorithms like bcrypt or Argon2. Crucially, always use unique “salts” with each password; this adds randomness to the hashing process and protects against “rainbow table” attacks (57).
For any sensitive API, implementing multi-factor authentication (MFA) is imperative. MFA requires users to provide at least two different forms of evidence to verify their identity. Microsoft data shows that MFA can reduce the risk of account compromise by an impressive 99.9% (58). _Validating and sanitizing all authentication inputs is vital to prevent various injection attacks (60)._
For mobile apps and single-page web applications, it is strongly recommended to use OAuth 2.0 with PKCE (Proof Key for Code Exchange). PKCE adds an extra security layer, preventing attacks where authorization codes might be intercepted in public clients (61).
Comprehensive logging and monitoring of authentication events are also crucial. This means recording every successful login, failed attempt, and token generation. These logs provide visibility for detecting potential security breaches and are invaluable during incident response (63). Finally, regularly rotating API keys and secrets—ideally every 90 days for high-security environments—is another key practice (64).
Common API Authentication Errors and Fixes
Despite careful implementation, errors are an inevitable part of development. Understanding these common technical glitches, misconfigurations, and coding mistakes is vital for maintaining smooth API operations (66, 67).
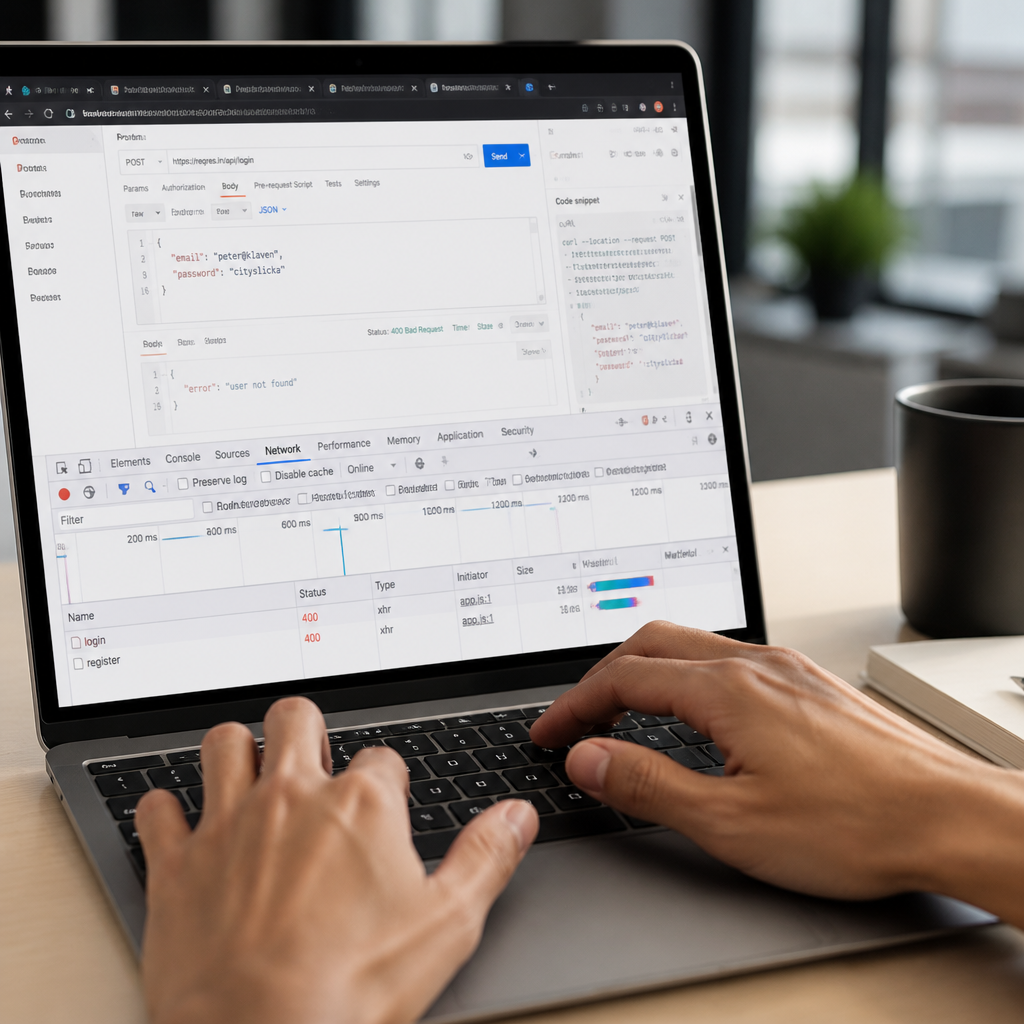
One of the most frequent errors is the 401 Unauthorized HTTP status code. This indicates that your authentication credentials are invalid or missing. Common causes include sending an incorrect API key, using a malformed token, or attempting to use an expired token. To resolve this, always double-check the format of your credentials, ensure your token is still active, and verify that the Authorization header is correct (68).
In contrast to a 401, a 403 Forbidden error signifies that your authentication was successful, but you lack the necessary permissions (authorization) to access the specific resource. It’s like having a valid ID to enter a building but being denied access to the VIP lounge. The solution is to review the user’s roles, scopes, and access control policies (69).
Here is a list of other common authentication errors and their solutions:
- “Invalid API Key”: Ensure the key is active, copied accurately, and contains no hidden spaces.
- “Token Expired”: Implement logic to detect expired tokens and automatically request a new one using a refresh token. Also, confirm system clocks are synchronized.
- “CORS Error”: The API server must be configured to allow requests from your website’s domain by including specific
Access-Control-Allow-Originheaders. - “Invalid Signature” (JWTs): This indicates the token has been tampered with or there’s a mismatch in the secret key or algorithm used for signing and verification (70).
Regarding JWT “Invalid token signature” errors, they typically mean the wrong secret key was used for signing, the algorithm settings differ, or the token has been altered. The primary fix is to meticulously verify that the secret key and signing algorithm configurations are identical where the token is created and where it is validated (71).
CORS (Cross-Origin Resource Sharing) errors occur when a web page attempts to make a request to an API on a different domain. To resolve this, the API server must send back specific HTTP headers like Access-Control-Allow-Origin to indicate which domains are allowed to access its resources (72).
For effective troubleshooting, your browser’s developer tools (especially the Network tab) and dedicated API testing tools like Postman are invaluable. These tools provide a deep look into the data, showing precisely which HTTP headers and response messages are being sent and received (73).
An often-overlooked issue is clock skew. This happens when the system clocks of your client and server are not synchronized. For time-sensitive tokens like JWTs, even a slight difference can cause valid tokens to be rejected. The solution is to ensure all systems use Network Time Protocol (NTP) for accurate clock synchronization and to incorporate a small “tolerance window” in your validation logic (74).
FAQ
Q1: What is the primary difference between API authentication and authorization?
A1: API authentication verifies who you are (your identity as a user or application). API authorization, conversely, determines what you are allowed to do or what resources you can access after your identity has been confirmed. Authentication always precedes authorization.
Q2: Why is HTTPS/TLS encryption considered a best practice for API authentication?
A2: HTTPS/TLS encryption establishes a secure, encrypted tunnel for all communication between the client and the API server. This protects sensitive data, such as credentials and authentication tokens, from interception or tampering by malicious actors during transmission, guarding against attacks like “man-in-the-middle.”
Q3: What are JSON Web Tokens (JWTs) and why are they popular for API authentication?
A3: JWTs are self-contained authentication tokens composed of three parts: a header, a payload (containing user information), and a cryptographic signature. They are popular because they enable “stateless” authentication, meaning the server doesn’t need to store session data. The server can quickly validate the token’s integrity by verifying its signature, making them efficient and scalable for distributed systems like microservices.
Q4: What is the significance of token expiration and refresh mechanisms in API security?
A4: Token expiration and refresh mechanisms are crucial for limiting security exposure. Short-lived access tokens (e.g., 15–60 minutes) minimize the risk if a token is compromised. Longer-lived refresh tokens are then used securely to obtain new access tokens once the current one expires, allowing continuous access without frequent re-authentication. This approach balances strong security with a smooth user experience.
Q5: What does a “401 Unauthorized” error typically indicate, and how can it be fixed?
A5: A “401 Unauthorized” error explicitly signals that the client’s authentication attempt failed. This is usually due to missing, invalid, or expired credentials or tokens. To fix it, verify that your authentication credentials are correctly formatted, the token is valid and not expired, and the Authorization header is properly included in the request.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.