what is api testing in software: 5 Powerful Insights
Imagine an e-commerce application failing during checkout. Traditional UI tests that mimic user interactions show nothing wrong, yet customers report errors. The issue often lies hidden in the communication between different software components—a problem perfectly suited for API testing to uncover. In today’s fast-paced software world, ensuring applications function perfectly is crucial, and understanding how these internal pieces interact is key.
API testing is a type of software testing that focuses on examining Application Programming Interfaces (APIs). Think of an API as a waiter in a restaurant: you tell the waiter what you want, and they bring your order from the kitchen. In software, one part of an application communicates its needs to another part through an API. This form of testing works directly with these messages, bypassing the user interface to confirm that APIs are dependable, performant, and secure.
Essentially, this process examines the core logic of the software. Instead of interacting with on-screen buttons and forms, testers send direct requests to an API and analyze the responses. This verifies communication between software components, often using protocols like REST, SOAP, GraphQL, and gRPC. The importance of this “behind-the-scenes” approach is increasingly recognized, with 82% of development teams now using it in their automated processes, according to a 2023 SmartBear report. This adoption is largely due to its efficiency, as it can catch problems significantly faster than traditional UI testing.
Let’s discover why this testing methodology is not just beneficial but essential for building robust, efficient, and secure software.
A 2024 study in the Journal of Systems and Software found that thorough API testing led to a 64% reduction in post-release bugs and a 47% faster problem resolution time.
Many top software experts advocate for this approach. Martin Fowler, Chief Scientist at ThoughtWorks, strongly recommends placing API or “service” tests at the core of the “testing pyramid” model. He believes these tests offer more value than UI tests because they directly verify critical business rules, run much quicker, are less prone to breaking with minor visual changes, and are generally easier to maintain. Testing covers a broad range of checks, including verifying status codes, ensuring correct data formats, confirming quick response times, testing error handling, and validating data accuracy.
API Testing Fundamentals in Software
What are the types of api testing in software development?
This form of testing is not a single activity but a collection of different tests, each designed to verify a specific aspect of an API. This multi-faceted approach ensures an API is not only functional but also reliable, performant, and secure under various conditions. Understanding these types is key to developing a sound strategy.
- Functional Testing: This fundamental type checks that API endpoints return the correct and expected responses for the data sent. It includes positive scenarios with valid data, negative scenarios with invalid data to ensure proper error handling, and boundary value analysis to test the API’s limits.
- Load and Performance Testing: These tests are crucial for assessing how an API behaves under concurrent user activity. They measure response times, throughput (requests per second), and latency, helping to identify performance bottlenecks. A more extreme form, stress testing, pushes APIs beyond their normal limits to discover breaking points.
- Security Testing: This critical area focuses on uncovering vulnerabilities that could be exploited. It involves looking for common threats such as injection attacks, authentication flaws, and sensitive data exposure, often aligning with guidelines like the OWASP API Security Top 10.
- Integration Testing: This verifies that different API endpoints or services work together correctly as a cohesive system. It is particularly important in complex microservices architectures where multiple small components collaborate.
- Contract Testing: Increasingly important in modern systems, contract testing uses tools like Pact to verify an “agreement” between an API (provider) and its applications (consumers). This ensures that as individual services evolve, interfaces remain compatible.
- Fuzz Testing: Also known as “fuzzing,” this involves sending malformed, unexpected, or random data to API endpoints to uncover crashes, memory leaks, and security flaws that might not surface with typical test cases.
How api testing works in software engineering
API testing in software engineering follows a clear process: sending requests to an API and carefully examining the responses. This involves constructing HTTP or HTTPS requests with specific details, such as parameters, headers, and a request body, then checking the received responses against expected outcomes.
The typical workflow adheres to a structured plan. It begins with understanding the API’s specifications, often documented using standards like OpenAPI. Next, the testing environment is set up. _A misconfigured environment can lead to unreliable test results._ “Test data” and authentication mechanisms (like API keys) are then established. Once prepared, API calls are made with various inputs, and the responses are validated using “assertions.” Finally, all test results are logged in detailed reports.
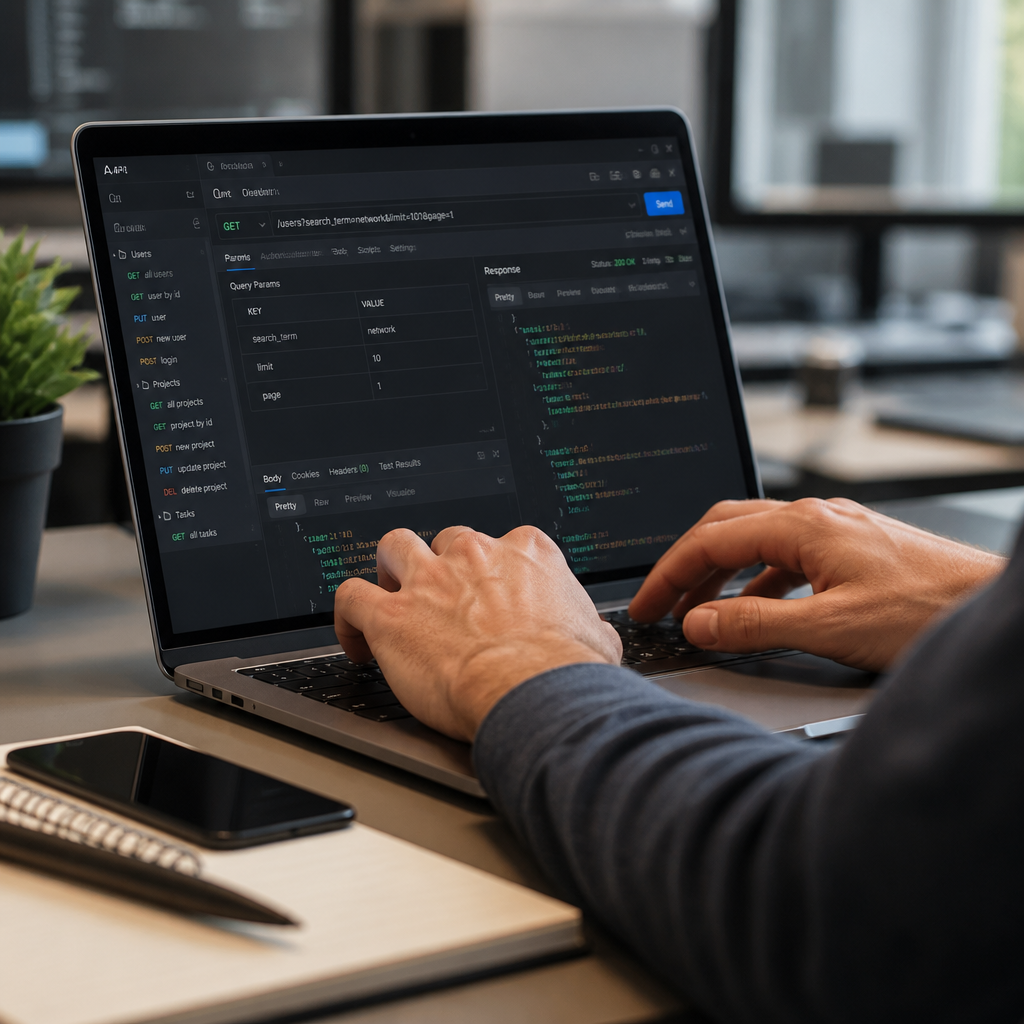
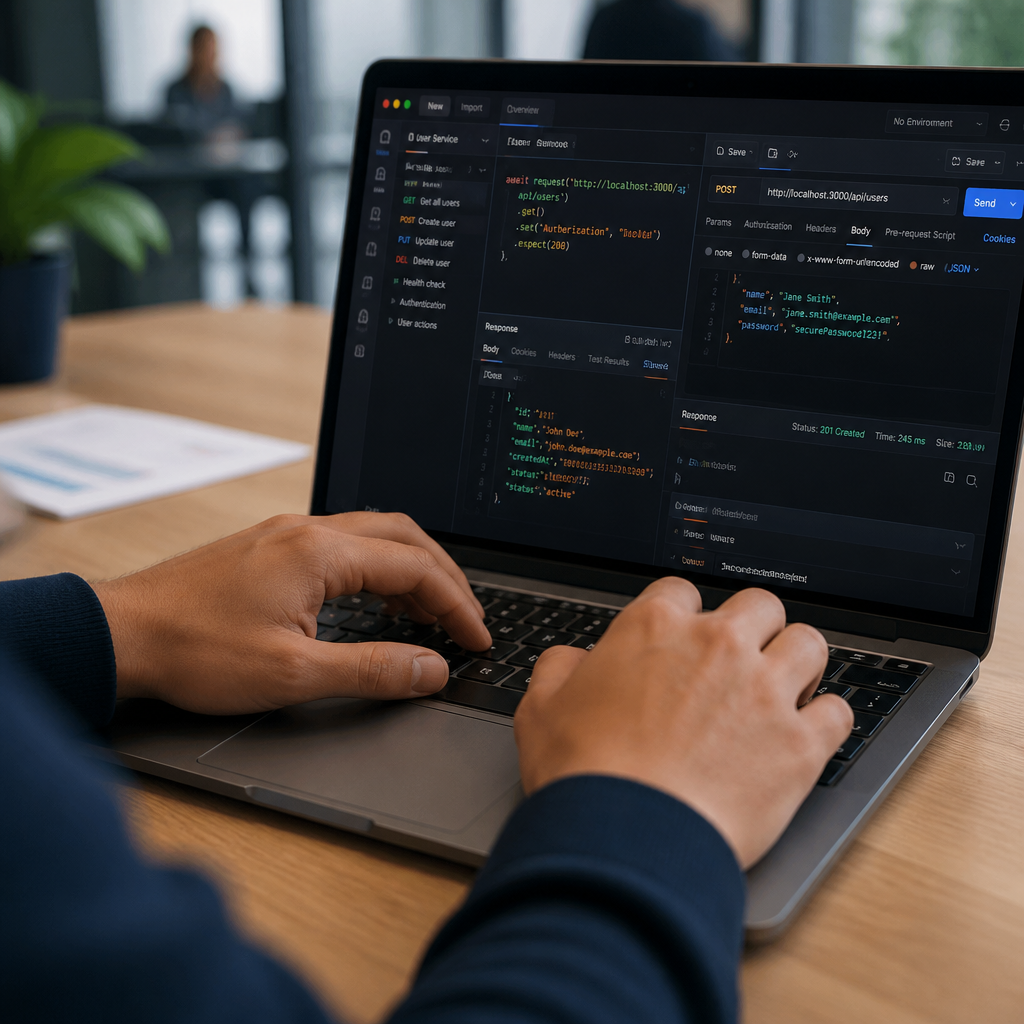
API requests consist of a method (e.g., GET, POST), endpoint URL, headers, query parameters, and a request body. The API sends back a status code, response headers, and a response body. Authentication is also rigorously tested to ensure only authorized users can access sensitive functions. The power of this method is amplified through automation, with research indicating that automated tests catch a high percentage of integration problems before release. Verifying the response is a multi-step process that includes schema validation, data validation, status code verification, and performance validation.
James Bach, a respected software testing expert, emphasizes the importance of understanding an API’s “state model” for effective testing. This involves recognizing how each request can alter the system’s current condition and how subsequent requests might depend on those changes.
This state-aware approach differentiates interface testing from much UI testing. Modern API testing is also a cornerstone of CI/CD pipelines, where tools automatically run tests with every code change for early issue detection.
API Testing Tools and Best Practices in Software Development
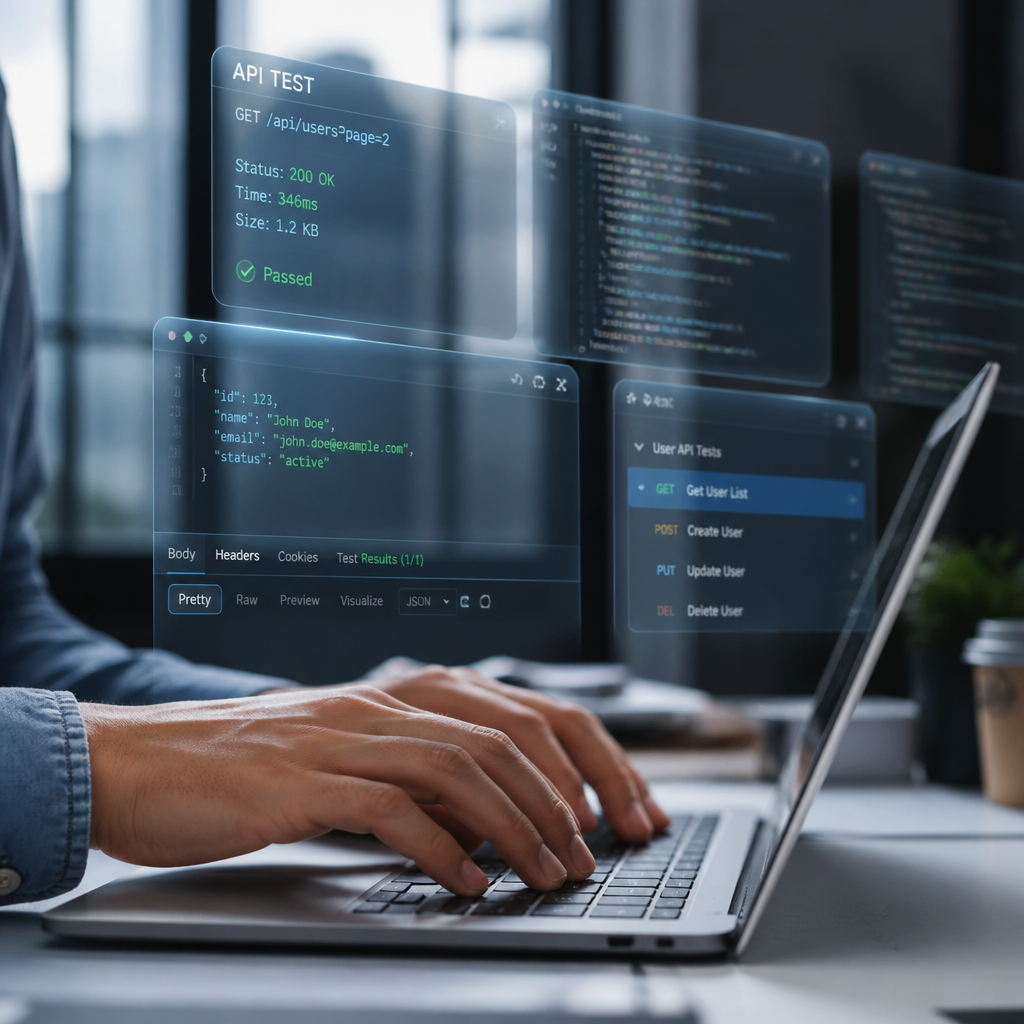
What api testing tools are used in software testing?
Tools for this purpose are specialized applications that streamline the creation, execution, and management of tests for application programming interfaces. These tools range from simple request-sending utilities to comprehensive automation frameworks. The choice of tool often depends on project requirements, team expertise, and API complexity.
- Postman: A leading tool used by millions of developers, it provides an intuitive interface for building and sending API requests, organizing them into collections, and automating tests using JavaScript.
- REST Assured: A powerful Java library for testing REST APIs. It offers a domain-specific language (DSL) that simplifies the creation of readable and maintainable test code.
- Apache JMeter: An excellent option for performance testing, JMeter can simulate thousands of concurrent users to measure response times, throughput, and latency.
- SoapUI: A well-established tool for testing both SOAP and REST APIs, it provides a comprehensive feature set, including functional, security, and load testing capabilities.
Angie Jones, a notable figure in developer relations, advises selecting tools that align with an organization’s existing technology stack and team skill sets. Other noteworthy tools include Karate DSL, which combines API testing and UI automation; Insomnia, an open-source API client; and enterprise-level platforms like Katalon Studio and Tricentis Tosca.
API testing best practices in software development
Effective interface verification relies on adhering to best practices that maximize value and ensure smooth integration into the software development lifecycle. These practices promote robust, maintainable, and reliable tests.
A central concept is the testing pyramid, which advocates for a large base of unit tests, a moderate middle layer of integration tests, and a small top layer of UI tests. These tests occupy a strategic middle ground, offering a balance of speed, reliability, and coverage. Comprehensive test coverage is vital, extending beyond the “happy path” to include negative scenarios and error handling.
Tests should be independent and idempotent, meaning they are self-contained and produce the same result regardless of how many times they are run. Using environment-specific configurations allows teams to switch between development, staging, and production environments easily. _Importantly, sensitive information like API keys should always be stored securely, never hardcoded in test scripts._ Data-driven testing, where tests use multiple sets of input data, enhances coverage with less code.
Integrating API testing into CI/CD pipelines is fundamental for modern development. Automatically running tests with every code change ensures that regressions are caught early. In microservices architectures, contract testing is essential to ensure compatibility between services. Finally, maintaining clear test documentation and detailed logging facilitates efficient debugging and long-term maintainability.
API Testing Value and Comparisons in Software Quality
Benefits of api testing in software quality assurance
This type of verification offers numerous benefits that significantly enhance software quality, making it an indispensable practice in modern development. These advantages span the entire development lifecycle.
One of the most significant benefits is early defect detection. This form of testing allows teams to validate core business logic directly, without a fully developed user interface. Catching bugs earlier leads to substantial cost savings; _problems identified during early stages can be up to 15 times cheaper to fix than those found after release._ Faster execution is another considerable advantage, as interface tests typically run much more quickly than UI tests, providing rapid feedback.
This method also provides superior test stability and maintainability because APIs tend to evolve less frequently than user interfaces. This approach enables comprehensive coverage of business logic paths that might be difficult to reach through the UI alone. Its language and platform independence ensure consistent operation across all clients (web, mobile, IoT). From a security perspective, dedicated security testing can identify weaknesses early in development. These combined benefits establish API testing as a cornerstone of modern software quality assurance, leading to more reliable and secure products.
API testing vs unit testing in software
While both API testing and unit testing are crucial components of a robust software quality strategy, they differ significantly in their objectives and the levels at which they operate within the software architecture. Understanding these distinctions is key to planning a balanced and effective approach.
Unit testing focuses on verifying individual pieces of code—such as functions or methods—in isolation, typically mocking external dependencies. In contrast, interface verification checks how multiple components interact through API endpoints, testing the system’s business logic as a cohesive unit. The table below highlights their key differences.
| Feature | Unit Testing | API Testing |
|---|---|---|
| Scope | Individual code units (functions, classes) | Interactions between components via APIs |
| Level | White-box (internal code structure) | Black-box (external behavior) |
| Speed | Very fast (milliseconds) | Slower (seconds) |
| Dependencies | Mocked or stubbed | Real or test instances |
| Failure Point | Specific code logic errors | Integration, configuration, or contract issues |
Martin Fowler’s Test Pyramid model suggests a large base of fast unit tests, a moderate number of integration tests in the middle, and a small number of end-to-end UI tests at the top. When a unit test fails, it points directly to a specific code location. An interface test failure, however, often indicates broader issues like integration problems or configuration errors. Both are essential, as unit tests alone cannot identify integration issues, and API tests may lack the granularity for pinpointing specific code logic errors.
In conclusion, interface testing is fundamental to modern software development, offering an efficient method to ensure the quality, reliability, and security of inter-component communication. By directly testing business logic without relying on the UI, it facilitates early bug detection, reduces problem resolution costs, and provides the rapid feedback crucial for continuous development. The various types of this testing—functional, performance, security, integration, and contract—provide a thorough examination of an API’s behavior. Supported by a robust ecosystem of tools and guided by best practices, this approach empowers development teams to build more resilient systems. While distinct from unit testing, API testing complements it by validating critical interactions, ultimately leading to higher-quality software.
FAQ
Q1: What is the main difference between API testing and UI testing?
A1: API testing checks the business logic and how software components communicate, like message exchanges, without a visual interface. UI testing, conversely, focuses on the application’s visual elements and user interactions. API tests generally run faster, are less susceptible to breaking from visual changes, and help find bugs earlier, often before the UI is fully developed.
Q2: Why is API testing considered more efficient than UI testing for finding defects?
A2: API testing is more efficient because it directly targets core software functions, bypassing the visual layer. This results in much faster test execution—sometimes 10 to 100 times quicker than UI tests. By detecting bugs earlier, API testing can significantly reduce the cost of fixes, potentially up to 15 times cheaper than post-release bug resolution, and provides prompt feedback to developers.
Q3: What are some common types of API testing performed in software development?
A3: Common API testing types include functional testing (verifying intended behavior), load and performance testing (assessing behavior under user load), security testing (identifying vulnerabilities), integration testing (checking component interactions), and contract testing (ensuring adherence to communication agreements, especially in microservices).
Q4: Can you name some popular tools used for API testing?
A4: Popular API testing tools include Postman (for building requests and test automation), REST Assured (a Java library for REST API testing), Apache JMeter (primarily for performance and load testing), SoapUI (for functional, security, and load testing of SOAP and REST APIs), and Insomnia (a developer-friendly API client).
Q5: How does API testing fit into a CI/CD pipeline?
A5: API testing integrates into CI/CD pipelines by automatically executing API tests whenever new code is committed, a change is proposed, or a deployment occurs. This establishes a continuous feedback loop, enabling teams to quickly identify new issues or regressions. Tools like Jenkins or GitHub Actions manage these automated runs, often executing tests in parallel for rapid results.