what is an api key: 7 Essential Facts for Safer APIs
When I was first learning web development, building a small app to display local weather, I hit a roadblock. My code couldn’t connect to the weather service, and I couldn’t figure out why. That’s when I discovered API keys. It felt like needing a secret password to get into an exclusive club. An API key is exactly that—a unique digital pass. It’s a special code, a mix of letters and numbers, that tells a web service, “Hey, it’s me! Let my app access your data.” This key serves as a unique identifier and a secret handshake, allowing your application to securely communicate with an Application Programming Interface (API). Without it, my weather app couldn’t fetch any data, and my project would have stalled.
Essentially, an API key acts as a unique digital ID that an application presents when it wants to interact with an API. Think of it as a special badge or a unique alphanumeric code that confirms your identity. This badge lets the API know that your program is authorized to make requests, ensuring that only approved applications or individuals can access its resources and data. This fundamental security measure helps maintain order and protection in our interconnected digital world.
The concept of API keys gained significant traction in the early 2000s, coinciding with the rise of web APIs as the primary method for different software systems to communicate. Early adopters like Google Maps required developers to obtain an API key to embed maps into their own websites or apps. This approach made it much easier for developers to integrate powerful services without having to build everything from scratch, paving the way for innovation. When your app sends a request to an API, the key is typically included within that request. It might be in a special “header” section, as part of the web address (known as a “query string parameter”), or within the main body of the request. The API server then swiftly checks this key against its records to verify your app’s identity and permissions before granting access to the requested information.
While API keys form a basic layer of API security, it’s important to recognize their limitations. For highly sensitive operations, such as financial transactions or handling personal health data, they aren’t as robust as more advanced security systems like OAuth 2.0. This is partly because API keys often have long lifespans, meaning a compromised key could grant an attacker ongoing access. Despite this, their ease of use and effectiveness for many common tasks make them a widely used tool for managing application-to-application communication. They are a critical piece of information that ensures data and features are shared securely and in a controlled manner between different software systems.
Understanding API Keys
API keys are more than just simple identifiers; they are crucial for how applications communicate securely and efficiently in today’s connected digital landscape. Their functions range from basic authentication and access management to monitoring API usage. Understanding these roles is vital for anyone developing or using applications that rely on external services.
What is an API key used for?
The primary role of an API key is to verify the identity of an application or user (authentication) and to confirm their authorization to perform a requested action (authorization) when accessing an API. This fundamental function ensures that only approved parties can make requests to protected resources, effectively acting as a gatekeeper for the API’s features and data. Without this verification, an API would be vulnerable to data leaks or service disruptions. By requiring a unique key, API providers can clearly identify each calling application and control who interacts with their services.
Beyond identity verification, API keys are extensively used by providers for tracking usage. This involves monitoring and analyzing how the API is being accessed—tracking the number of requests, their frequency, and which specific API components (“endpoints”) are being utilized by different applications. This data enables providers to implement “rate limits,” preventing any single application from overwhelming the API with excessive requests. This ensures fair use and keeps the service stable for all users.
API keys also play a significant role in establishing “granular access control.” Providers can use keys to define different access levels. A basic subscription might grant a key holder “read-only” access, while a premium plan could offer full “read-write” capabilities. This capability allows API providers to tailor access based on subscription tiers, partnership agreements, or specific project requirements. For APIs that are monetized, keys are indispensable for billing and enforcing usage quotas, enabling providers to accurately track usage for billing purposes.
What is an API key and how does it work?
An API key functions within a standard “request-response cycle,” the fundamental mechanism for application-to-web service communication. When your client application needs data from an API, it includes its unique API key in the HTTP request. The key can be sent in the request “header,” typically under a field like X-API-Key, or as a “query parameter” within the URL itself. Upon receiving the request, the API server first checks the provided key. It searches its database to confirm the key is valid, active, and associated with a legitimate account. _If the key is approved, the server then verifies the key’s permissions and any applicable rate limits before returning the requested data or an error message._
The process of obtaining an API key usually begins when a developer registers for access to a service provider’s API. During this registration, the provider’s system generates a “cryptographically random string”—a complex, unpredictable sequence of characters that is unique to the developer. This key is then securely stored in the provider’s database, linked to the developer’s account.
A complete API key system involves several interconnected components. Beyond the API key itself, “metadata” defines its characteristics and limitations, such as its creation date, specific permissions, and rate limits. “Usage logs” record every API interaction associated with a key, which is essential for monitoring, billing, and security analysis. For improved security, keys might be stored as “hashed values,” or more complex methods may employ “HMAC (Hash-based Message Authentication Code) signatures” where the key cryptographically “signs” the entire request. This signature allows the API server to verify not only the caller’s identity but also that the request has not been tampered with during transit.
Types of API keys
API keys are not uniform; they exist in various forms, each designed for specific scenarios and security requirements. Understanding these differences is crucial for developers to use them correctly.
- Public or Client-Side API Keys: These keys are intended for use in applications that run directly on a user’s device, such as mobile apps or web browsers. They typically have very restricted permissions, such as “read-only” access to non-sensitive, public data. _The inherent risk of these keys being extracted from client-side code necessitates these strict limitations to minimize potential damage if they are compromised._
- Private or Secret API Keys: These are meant to be kept strictly confidential and stored on secure servers. These keys generally possess full access permissions, including the ability to modify data and access sensitive information. A critical security rule is that private keys are never exposed in client-side code, as their compromise can lead to significant security breaches.
- Restricted API Keys: This category represents keys where specific limitations are imposed to enhance security. Restrictions can include limiting usage to specific IP addresses, certain website domains (HTTP referrers), or confining a key to accessing only certain features of the API.
- Development vs. Production Keys: Many providers issue separate keys for development and live environments. This allows developers to build and test applications in a sandbox environment without impacting live user data or incurring production charges.
- Time-Limited Keys: These are temporary credentials that automatically expire after a defined period. They are frequently used for trial access or in situations demanding high security, as their short lifespan significantly reduces the window of vulnerability.
Obtaining and Managing API Keys
Acquiring and effectively managing API keys is a foundational step for any developer intending to connect with external services. The process involves interacting with a provider’s developer website, followed by careful integration into your application’s security strategy.
How to get an API key?
The process of obtaining an API key is generally straightforward and begins on the API provider’s dedicated “developer portal.” While specific steps vary between providers like Google Cloud, AWS, or Stripe, the general workflow is as follows:
- Create a Developer Account: Register an account with the API provider, which often requires email verification and agreement to the terms of service.
- Create a Project or Application: Within the provider’s console or dashboard, create a new project or register your application. This serves as a container for your API connections.
- Enable the Required API Services: Activate the specific API services your application needs.
- Generate Credentials: Proceed to the “API Keys” or “Credentials” section to generate the key.
- Securely Store the Key: Copy the generated key and store it securely. This last step is crucial, as improper handling of the key from the outset can lead to significant security weaknesses later on.
After obtaining a key, it’s a good practice to test it with a simple API call to confirm it is active and has the necessary permissions before integrating it into your main application.
API key vs API token
While often used interchangeably, API keys and API tokens have fundamental distinctions in their design, security, and usage.
At its core, an API key is a static, long-lasting identifier used to authenticate an application or project. In contrast, an API token (like an OAuth 2.0 token) is a temporary, session-based credential that authenticates a specific user and has a limited lifespan. _This difference between a static identifier for an application and a dynamic, user-specific credential is a core distinguishing factor._
| Feature | API Key | API Token (e.g., OAuth 2.0) |
|---|---|---|
| Purpose | Identifies the calling application/project | Authorizes a specific user for a limited time |
| Lifespan | Long-lived; valid until manually revoked | Short-lived; expires automatically (minutes/hours) |
| Security | Less secure for user-centric actions | More secure due to short life, scopes, and revocability |
| Use Case | Server-to-server, internal services | User-facing apps (mobile/web), user-specific actions |
| State | Static | Dynamic; can be refreshed or revoked |
According to Philippe De Ryck, founder of Pragmatic Web Security, “API keys are identifiers, not authentication credentials. They tell you who is calling, but not whether they should be allowed to call. Tokens, especially JWTs with proper signatures, provide both identification and authorization in a cryptographically secure manner.”
This expert view emphasizes that tokens are generally preferred for scenarios requiring dynamic, user-centric security, while keys are suitable for identifying applications in server-to-server communication.
API Key Security and Best Practices
Maintaining the security of API keys is paramount for preventing unauthorized access, data breaches, and service misuse. Adhering to established security protocols can significantly mitigate the associated risks.
How to keep an API key secure?
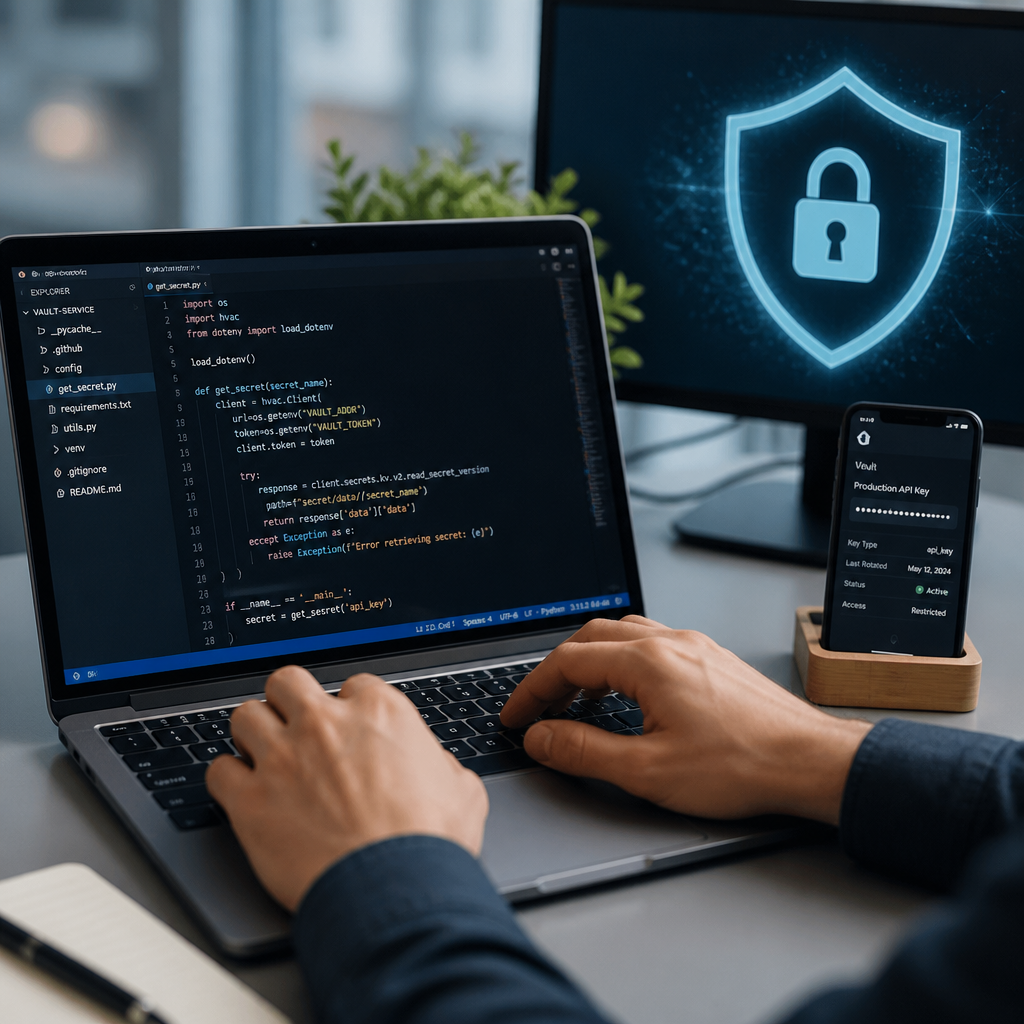
A critical aspect of API key security involves proper storage and transmission. _A core rule is that developers should never hardcode API keys directly into their source code._ Hardcoding makes keys easily discoverable if the code is compromised.
Instead, follow these key security measures:
- Use Secure Storage: Store API keys in environment variables, secure configuration files outside your web root, or specialized secrets management systems like HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault.
- Secure Version Control: Add configuration files containing keys to your
.gitignorefile to prevent them from being accidentally committed to public or private code repositories. - Encrypt Transmission: Always transmit API keys over HTTPS/TLS encrypted connections to protect them from interception. Avoid passing keys in URL query parameters, where they can be logged in browser history or server logs.
- Implement Access Restrictions: Use IP whitelisting to restrict key usage to specific IP addresses and HTTP referrer restrictions for browser-based applications. Apply the “principle of least privilege” by granting keys only the minimum permissions required.
- Rotate Keys Regularly: Regular key rotation, such as every 90 days, is a critical security practice. This limits the damage if a key is compromised, as its valid duration is restricted.
- Monitor and Alert: Set up monitoring and automated alerts for unusual usage patterns, such as sudden request spikes or access from unexpected locations, to enable a swift response to threats.
API key best practices
Implementing a comprehensive set of best practices involves strategic management throughout the entire key lifecycle to optimize both security and operational efficiency.
According to Daniel Miessler, a cybersecurity expert, “The best API key is one that doesn’t exist. Whenever possible, use more modern authentication methods like OAuth 2.0 or mutual TLS. When you must use API keys, treat them like passwords: unique, rotated regularly, and never shared.”
When you must use them, follow these best practices:
- Use Distinct Keys: Employ separate API keys for different applications and environments (development, testing, production). This practice, known as key segregation, isolates the impact of a potential compromise.
- Maintain an Inventory: Keep a detailed inventory of all API keys, including their purpose, associated applications, permissions, and creation dates. This is essential for effective management and auditing.
- Enforce Rate Limits: Configure appropriate rate limits for each key to prevent misuse and protect your service from denial-of-service scenarios.
- Enable Audit Logging: Maintain comprehensive logs of all API key usage, capturing timestamps, endpoints accessed, and source IP addresses. These logs are invaluable for security analysis and troubleshooting.
- Educate Developers: Provide clear documentation and training for developers on security best practices, highlighting common mistakes like hardcoding keys and the importance of secure storage.
- Have a Revocation Plan: Establish a clear and swift procedure for revoking compromised keys immediately upon detection to minimize potential damage.
In summary, API keys are a fundamental tool for controlling access to digital services. While they offer simplicity, their nature as long-lived credentials necessitates a diligent approach to security. By understanding the different types of keys, adhering to best practices, and implementing robust security measures, developers can leverage the power of APIs while safeguarding their valuable data and services.
FAQ
Q1: What is the primary difference between an API key and an API token?
An API key is typically a static, long-lived string used to identify and authenticate an application or project, granting it access to an API. An API token, especially an OAuth token, is usually a temporary, session-based credential that authenticates a specific user within an application’s context and often has a limited lifespan, making it more dynamic and generally more secure for user-specific operations.
Q2: Why is it considered a security risk to hardcode API keys directly into source code?
Hardcoding API keys directly into source code makes them easily discoverable if the code repository is compromised, accidentally made public, or even if the application is reverse-engineered. This exposure can lead to unauthorized access to the API, potential data breaches, and service abuse. Best practices recommend storing keys in environment variables or dedicated secrets management systems.
Q3: What is the “principle of least privilege” in the context of API keys?
The principle of least privilege, when applied to API keys, means granting a key only the minimum permissions necessary for its intended function. For example, if an application only needs to read public data, its API key should not have permissions to write data or access sensitive administrative functions. This limits the potential damage if the key is compromised.
Q4: How often should API keys ideally be rotated?
While specific recommendations can vary, it is commonly suggested to regularly rotate API keys, with a frequent recommendation being every 90 days. Regular rotation helps to limit the impact of a potential compromise by ensuring that even if a key is leaked, its valid period is finite, thereby reducing the window of vulnerability.
Q5: Can API keys be used for billing and quota enforcement?
Yes, API keys are widely used by commercial API services for billing and quota enforcement. Each key can be associated with a specific account, allowing providers to accurately track API usage for billing purposes and to enforce predefined quota limits. This helps prevent abuse, manage infrastructure costs, and ensure fair usage across all consumers of the API.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.