How to Find API Endpoints: 7 Easy Methods That Work
Have you ever wondered how your favorite apps, like a social media feed or an online shopping cart, magically update with new information without refreshing the entire page? It’s something I often thought about when I first started tinkering with web development. A few years ago, I was building a simple project that needed to pull data from a public weather service. I quickly realized that the magic behind this constant flow of information is something called an Application Programming Interface, or API. Think of an API as a waiter in a restaurant: you, the customer, tell the waiter what you want (e.g., “get me a weather forecast”), and the waiter goes to the kitchen (the server) to get it for you and brings it back.
An API endpoint is like a specific dish on that menu, or more accurately, a specific URL (a web address) where an API can access the resources it needs. It’s the exact spot where your application “talks” to a server to get or send data. For instance, an endpoint might look like https://api.example.com/users (to get a list of users) or https://api.example.com/products/{id} (to get details for a specific product). These endpoints are the crucial touchpoints in the interaction between an application and a server.
Each endpoint is designed to work with a particular HTTP method, which is essentially the “action” you want to perform. Common methods include GET (to retrieve data), POST (to create new data), PUT (to update data), DELETE (to remove data), or PATCH (to partially update data). Modern web applications, especially those that feel super smooth and fast, often use many endpoints, usually organized in a RESTful structure. This just means they follow a set of guidelines where each endpoint typically corresponds to a distinct resource or collection of resources. Understanding these basic components unlocks many web development mysteries.
Discover why finding these API endpoints is a really important skill for many people. If you’re a developer, it’s essential when you want to connect your app to other services (like adding a map from Google or payment processing from Stripe). For security experts, finding undocumented or “hidden” endpoints is crucial for testing, as they can sometimes be like unlocked back doors, creating significant security holes. In fact, a major cybersecurity organization called OWASP (Open Web Application Security Project) stresses that knowing how to find API endpoints is a critical first step in keeping APIs secure. These endpoints can be either documented (meaning they’re openly listed in official guides) or undocumented (they exist but aren’t officially published). A study in 2021 even found that about 23% of web applications have undocumented API endpoints that can be found using automated tools. This skill has proven incredibly useful for both building and securing projects.
Methods to Find API Endpoints in a Website
How to Find API Endpoints in a Website
Finding API endpoints within a website means figuring out the specific web addresses that an app uses to communicate with its servers in the background. This usually involves looking at the network traffic your browser sends and receives, checking JavaScript files, or even reading the basic HTML code of the page for embedded API calls. Modern websites, especially those that load quickly and feel like desktop apps (often called Single Page Applications, or SPAs, built with tools like React, Vue, or Angular), rely heavily on these API calls. These calls are often quite visible and can be tracked using special tools built right into your web browser.
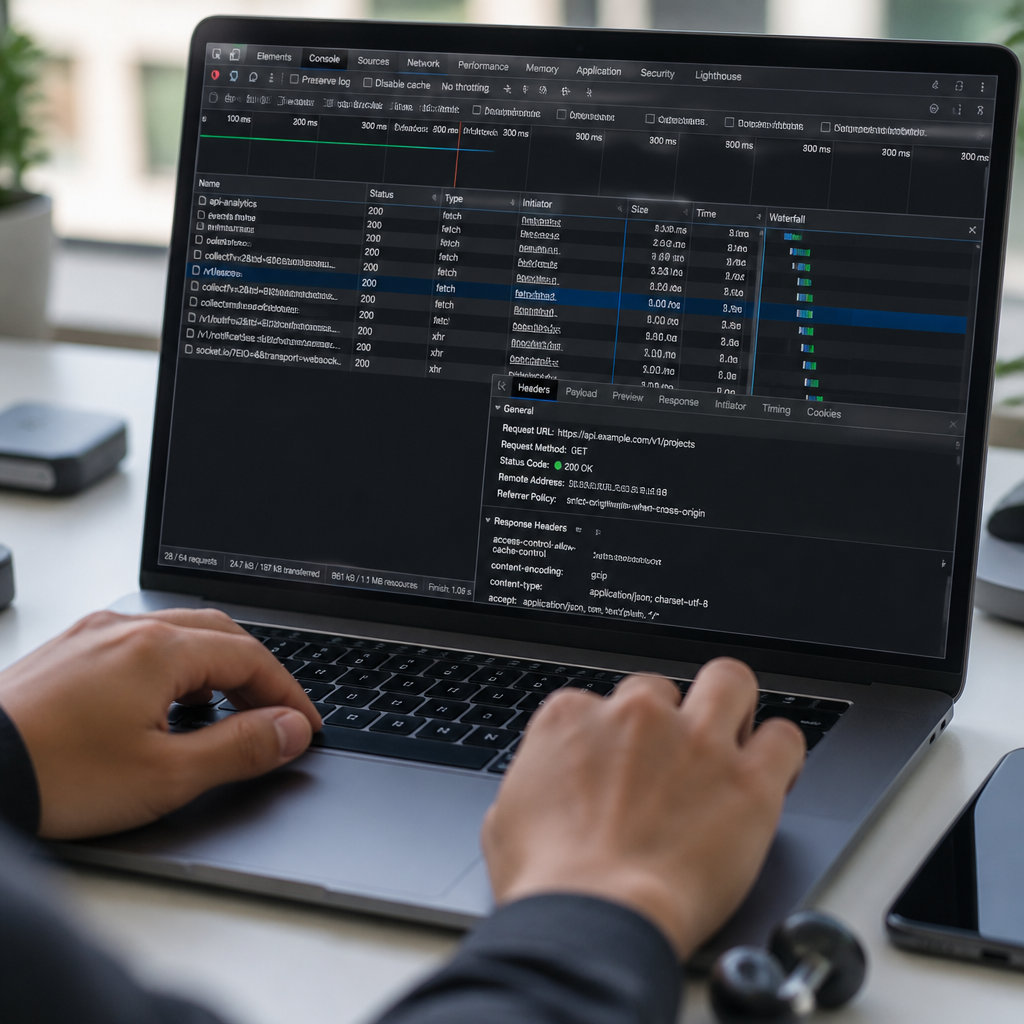
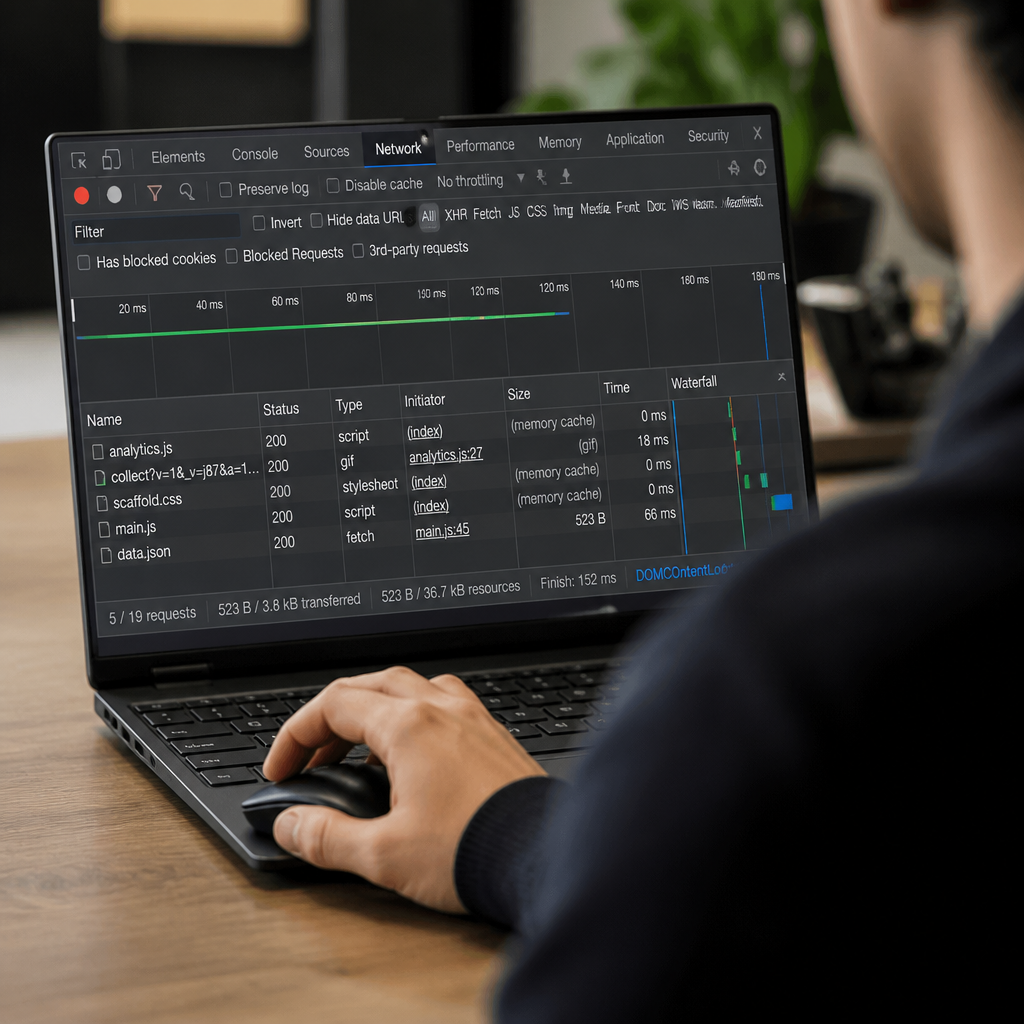
One of the easiest and most direct ways to see API endpoints in action is by using the “Network” tab in your browser’s developer tools. This handy tool catches all the requests your webpage makes, showing you the API endpoints as they’re called whenever you click buttons, fill out forms, or scroll to load more content. It’s like having a live log of all the conversations your browser is having with the server. This real-time view lets you see the exact URLs and the actions (like GET or POST) being used.
When hunting for API endpoints, look for certain URL patterns that serve as strong clues. Recognizing these patterns can really speed up your search. For instance, if you spot a request going to https://example.com/api/v1/users, you can be pretty confident that /api/v1/users is an API endpoint. Getting good at spotting these patterns comes with practice.
- Common Prefixes:
/api/,/v1/,/v2/,/rest/, or/graphql - Resource Paths:
/users,/products, or/data
Beyond watching live network traffic, you can also look at the website’s files themselves. JavaScript files, which are a huge part of almost all modern web applications, often contain the exact API endpoint URLs or general base URLs written directly into their code. You can find these by carefully looking through the source code.
Katie Paxton-Fear, a well-known security researcher, emphasizes that checking JavaScript “bundle” files (where many JavaScript files are combined into one for faster loading) is one of the best ways to find API endpoints. She points out that modern apps often put these API routes directly into the code that runs on your computer, making these files a treasure trove of information.
Sometimes, even public files like robots.txt and sitemap.xml can accidentally reveal API endpoint paths that developers might have wanted to keep private. While these files are mainly for search engines, they can sometimes list directories or specific endpoints, offering hints about their existence. By combining these different methods—watching live network traffic, examining JavaScript code, and checking public configuration files—you can get a really good picture of how a website’s APIs are structured. This approach helps identify both the obvious and the not-so-obvious endpoints, which is vital for building, testing, and securing applications.
How Can You Find API Endpoints Using Browser Developer Tools?
Browser developer tools are like a secret weapon for anyone who wants to understand how a website actually works. These tools, built right into popular web browsers like Chrome, Firefox, Edge, and Safari, have powerful features that let you watch and capture all the conversations (HTTP requests) a webpage has, including API calls, in real-time. This makes them a primary way to find API endpoints without needing any extra software. This is where most people start almost every time they’re trying to understand a new web application.
To access these developer tools, you can usually just press the F12 key on your keyboard. Another common way is to right-click anywhere on a webpage and choose “Inspect” from the menu. Once the developer tools pop up, you’ll want to click on the “Network” tab. This tab will immediately start recording all the network activity as you use the webpage. Each line you see in the Network tab gives you a ton of information: the web address (URL) of the request, the HTTP method used (like GET or POST), whether the request was successful (the “status code”), what type of data was received (e.g., JSON, HTML), how big the data was, and how long it took.
To really focus on API calls, the Network tab has helpful filtering options. Filtering requests to show only “XHR” (XMLHttpRequest) and “Fetch” requests is common. This helps clear out all the clutter like images, style sheets (CSS files), and fonts, letting you quickly zero in on the important API interactions. As you click around a website—hitting buttons, sending forms, or scrolling to load more content—you’ll see new API calls appear in the Network tab, giving you a dynamic view of how the application communicates.
A super useful tip is to enable the “Preserve log” option. When this is on, the network activity log won’t disappear if you go to a different page or if the page redirects. This prevents you from losing valuable API endpoint information during page changes.
Clicking on an individual request in the Network tab shows even more details. You can look at the “request headers” (information sent with your request, like who you are or what kind of data you expect), “response headers” (information about the server’s reply), the “request payload” (the actual data you sent to the server, especially for POST or PUT requests), the “response body” (the data you received from the API, like a list of products), and any “cookies” involved. This deep level of detail is absolutely vital for understanding how an API endpoint works, what kind of data it needs, and what kind of data it sends back.
For further analysis or testing, developer tools often have handy export options. The “Copy as cURL” feature, for instance, lets you export an API request as a command-line command. This can be used countless times to quickly paste a request into a terminal or into Postman, making it super easy to repeat and test the API call outside the browser. Chrome DevTools also has a “Copy all as HAR” option, which exports the entire network log into an HTTP Archive (HAR) file. This file can then be imported into other tools for deeper analysis or shared with team members for debugging. By really getting to know these powerful features, browser developer tools become an essential kit for anyone wanting to discover and understand API endpoints.
How to Find API Endpoints in Source Code
Digging into a website’s source code is another powerful way to uncover API endpoints. This approach involves carefully looking through the HTML, JavaScript, and various settings files to find URLs, API base addresses, and direct endpoint references that are built right into the client-side code (the code that runs in your browser). While browser developer tools show you live network traffic, analyzing the source code can reveal endpoints that might not be used during typical browsing, or it can give you a more complete, static picture of an application’s API structure.
The most basic step is to simply view the raw HTML of a webpage. You can usually do this by right-clicking on the page and choosing “View Page Source.” This raw HTML might have small blocks of JavaScript code embedded in it or references to separate JavaScript files. These scripts can sometimes directly contain API endpoint URLs or define variables that hold the main API address. While newer applications tend to keep things very organized, older or simpler websites might still have API calls directly inside the HTML.
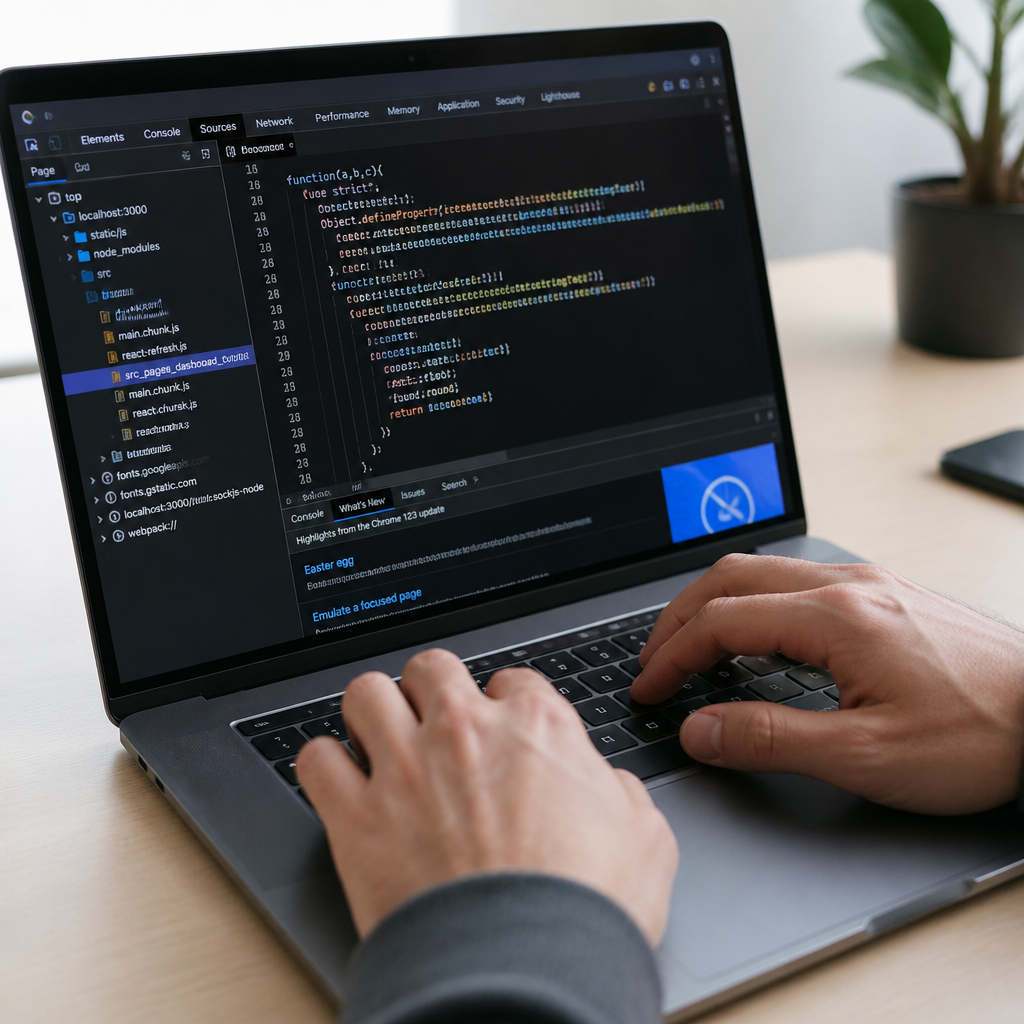
The “Sources” tab in your browser’s developer tools is where the real fun of source code analysis happens. Here, you can access all the JavaScript files that the webpage loads. Within these files, you can search for keywords that often point to API interactions. Useful search terms include “api”, “endpoint”, “fetch”, “axios”, “http”, or even the specific domain name of the website you’re investigating if you suspect it hosts API services. Modern web applications often use frameworks like React or Angular, and these typically define API services in dedicated files, such as api.service.js or http.service.ts, which centralize all the endpoint definitions. Finding these specific files can quickly lead you to a long list of endpoints. These are often the first places to look.
A common challenge when looking at JavaScript files is that they are often “bundled” and “minified” to make websites load faster. “Minification” removes all the extra spaces and shortens variable names, making the code hard to read. “Bundling” combines many different files into one. Luckily, developer tools offer a “Pretty print” button (often shown as {}), which can reformat (or “beautify”) this minified JavaScript code, making it much, much easier to read and understand. Once it’s readable, you can look for common JavaScript patterns that clearly define or call endpoints. For example, you might see fetch('https://api.example.com/endpoint'), axios.get('/api/users'), or const API_BASE = 'https://api.example.com'. These patterns directly reveal the structure and full URLs of API endpoints.
Beyond JavaScript, configuration files can also be a goldmine of API information. Files like config.js, environment.js, or even .env files (_if they’ve accidentally been exposed publicly_) often contain API base URLs, authentication keys, and other critical details about how endpoints are structured. These files are designed to manage settings specific to different environments (like testing vs. live websites), and their contents can provide a clear map of the API landscape.
To search efficiently across all loaded resources, developer tools provide a global search feature, usually by pressing Ctrl+Shift+F (or Cmd+Shift+F on a Mac). This lets you search for specific text or patterns across all HTML, CSS, and JavaScript files, as well as other resources loaded by the page. This is especially useful for finding a specific API base URL or a unique endpoint name that might be spread across several different files.
Daniel Miessler, a cybersecurity expert, highlights how effective examining JavaScript source code is for discovering API endpoints. He notes that developers sometimes leave comments, debug code, or even old, unused endpoints in the final versions of their apps, which can be incredibly valuable for discovery.
By systematically exploring the source code, you can uncover a significant part of a website’s API, helping with both development and security checks.
Tools and Techniques for Discovering API Endpoints
What is the Best Way to Find API Endpoints with Postman?
Postman is a super popular platform for building and testing APIs, offering a full set of tools that can really help you discover, document, and test API endpoints. It has features that range from capturing your browser’s web traffic to importing API specifications, making it a very flexible tool for different stages of managing APIs. Many people rely on Postman for countless projects, especially when they were first learning how to interact with different web services. It makes the process so much more approachable.
One of Postman’s most powerful features for finding endpoints is the Postman Interceptor. This is a small extension for your Chrome browser that captures all your browser’s web traffic and automatically turns that network activity into API requests right inside Postman. To use it, you first install the extension in your browser, then enable it within the Postman application (you’ll usually see a small satellite icon for it). Once it’s turned on, as you browse a website and click around, all the requests your browser makes are captured and show up in Postman’s “History” tab. This lets you see the exact API calls—including their URLs, methods (like GET or POST), headers, and the data they sent—as they happen in real-time. It’s an excellent way to quickly fill your Postman workspace with actual API requests from a live application.
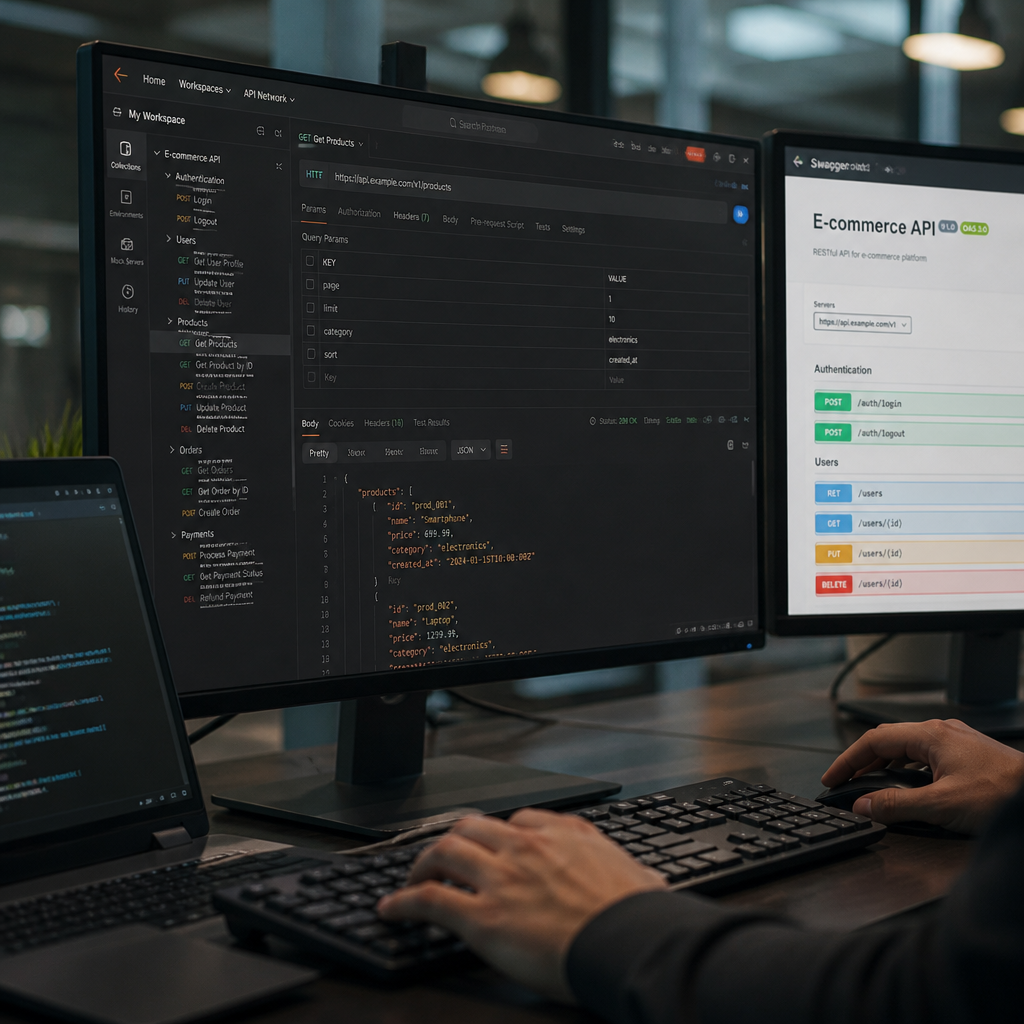
Postman is also fantastic at importing existing API documentation, which is often the easiest way to find a lot of endpoints at once. It supports various industry-standard formats, including OpenAPI/Swagger specifications, RAML, and GraphQL schemas. By importing these specifications, Postman can automatically create a “collection” (a group of related requests) that includes all the documented endpoints, complete with their expected inputs (parameters), the data they send (request bodies), and the structure of the data they return (response structures). This saves a huge amount of manual effort in setting up requests. The “Import” feature in Postman can even take a URL pointing to an API documentation file, allowing you to directly import endpoint definitions from services that publish their API specifications online.
Many companies and organizations publish official “Postman Collections” that contain their complete API endpoint structures. These collections are often shared publicly through the Postman API Network, which is like a big directory where developers can find and use collections from thousands of APIs. By exploring this network, you can find ready-made lists of endpoints for popular services, giving you a great head start in understanding and interacting with their APIs. Postman’s “Generate Collection from API” feature can also create a full collection by analyzing an OpenAPI specification file, further simplifying the process.
For testing, Postman’s “environment variables” are invaluable. They let you define placeholder values for common things like the main URL of the API, authentication tokens (like a password for the API), or API keys. This means you can test the same set of endpoints across different environments (for example, a development server, a staging server, or the live production server) simply by switching between these environments, rather than having to manually change the base URL for each request. This flexibility is really important for thorough testing and development. Postman is recommended to anyone serious about API work, regardless of their experience level.
Finally, the “Collection Runner” in Postman is a feature that can execute many endpoint requests one after another. This is particularly useful for finding out which endpoints are active, seeing how they respond, and running automated tests. By using Postman’s various capabilities—from capturing web traffic to importing documentation and running automated tests—users can efficiently discover, organize, and interact with API endpoints, making it a central tool in any API-focused workflow.
How to Find API Endpoints in REST API
REST (Representational State Transfer) APIs are designed following a specific set of rules that focus on making things simple, separating the client (your app) from the server, and using a standard way of communicating. In a REST API, endpoints are typically designed to represent “resources” (like users, products, or orders), and they are often organized in a logical URL structure with predictable patterns based on HTTP methods and resource names. Understanding these common patterns is key to finding endpoints within a RESTful system. When building a small e-commerce site, figuring out how to structure REST API endpoints felt like solving a puzzle, but once the patterns were understood, it clicked.
A core feature of RESTful APIs is their use of “noun-based naming” for endpoints. This means that the web addresses usually represent the things you’re working with, rather than the actions you want to perform. For example, you’ll commonly see endpoints like /users, /products, /orders, or /customers. When you want to interact with these resources, REST APIs use standard HTTP methods to specify what you want to do.
| HTTP Method | Action | Example |
|---|---|---|
| GET | Retrieve a resource or collection |
GET /users
|
| POST | Create a new resource |
POST /users
|
| PUT / PATCH | Update an existing resource |
PUT /users/{id}
|
| DELETE | Remove a resource |
DELETE /users/{id}
|
RESTful endpoint patterns often include “resource identifiers” to point to specific items within a resource. This leads to URLs like /users/{id} (to get a specific user by their ID), /products/{productId} (for a specific product), or /orders/{orderId}/items (to see items within a specific order). Many REST APIs also include “versioning,” often by putting a version number directly in the URL, such as /api/v1/users or /api/v2/products. This allows developers to update the API without breaking older applications that rely on the previous version.
The most reliable place to start looking for REST API endpoints is always the official documentation. The OpenAPI Specification (formerly known as Swagger) is the industry standard for describing REST APIs. You might find these at paths like /api/docs, /swagger-ui.html, or /api-docs on the API server. These interactive interfaces, often powered by tools like Swagger UI or ReDoc, let you explore all available endpoints, understand what they do, and even test them directly from your browser.
Beyond explicit documentation, the original ideas behind REST, laid out by its creator Roy Fielding, suggest that APIs should be “self-descriptive” with “hypermedia controls” (often shortened to HATEOAS). This means that API responses should ideally include links to related endpoints, allowing your application to discover and navigate the API just by reading the responses themselves. _While not all REST APIs fully implement HATEOAS_, it’s a principle that can help in discovery. Another technique involves using the OPTIONS HTTP method. Sending an OPTIONS request to a specific REST API endpoint can tell you which HTTP methods (GET, POST, PUT, DELETE, etc.) that endpoint supports. This can be very useful for understanding the full range of actions available for a given resource.
Finally, REST API endpoints for “nested resources” (resources that belong to another resource) often follow clear hierarchical patterns. For example, to get comments related to a specific post, you might see an endpoint like /posts/{postId}/comments. By understanding these common patterns and using documentation and interactive tools, you can effectively discover and understand the structure of REST API endpoints.
How to Find Hidden API Endpoints
Hidden API endpoints are those web addresses that aren’t officially documented but are still accessible. These endpoints can be like secret passageways, often representing significant security risks or exposing old features that developers might have forgotten about. Finding them is a critical job for security researchers, penetration testers (people who test systems for weaknesses), and even developers who want to make sure their API inventory is complete. Discovering a hidden endpoint always feels like finding a secret passage in a digital castle.
One of the most effective ways to find hidden endpoints is called “fuzzing.” Fuzzing involves systematically testing many different variations of known endpoint patterns by trying a wide range of inputs, often using “wordlists” (lists of common API paths and HTTP methods). Tools like Burp Suite, OWASP ZAP, and ffuf (Fuzz Faster U Fool) are designed to automate this process. They perform directory and parameter fuzzing to uncover endpoints that might not be immediately obvious. For example, if you know an API has /api/v1/users, a fuzzer might try /api/v1/admin, /api/v1/debug, or /api/v1/internal to see if any of these paths return a valid response.
Mobile applications are another fantastic place to discover hidden API endpoints. Mobile apps constantly communicate with backend APIs, and sometimes they use different or extra endpoints compared to the website version. By intercepting the network traffic of a mobile application (using tools like Burp Suite or OWASP ZAP as a proxy) or even “decompiling” the app’s package (like an APK for Android or IPA for iOS), you can uncover hardcoded API endpoints, authentication tokens, and backend URLs that might not be exposed anywhere else.
Public code repositories, such as GitHub, can also accidentally expose API endpoint information. Developers might unintentionally commit configuration files, documentation, or example code that contains base URLs, specific endpoint paths, or even sensitive API keys and passwords. Searching these repositories using specific keywords related to the company or application you’re looking at can sometimes reveal valuable clues. Similarly, the Wayback Machine (web.archive.org) can be used to view old versions of websites and API documentation. This can reveal endpoint references that have since been removed from current documentation.
“Google dorking,” a technique that uses advanced search operators, can also be used to find exposed API endpoints. By creating specific search queries like site:example.com inurl:api or site:example.com filetype:json, you might find publicly accessible API documentation, JSON files, or other resources that accidentally list endpoints.
From a security point of view, finding hidden endpoints is crucial because they often don’t have proper security checks, which can lead to problems like “Broken Object Level Authorization” (where you can access someone else’s data) or “Excessive Data Exposure” (where the API gives out too much information), as highlighted by the OWASP API Security Top 10. By combining these various methods, security professionals can significantly increase their chances of uncovering hidden API endpoints and figuring out their potential risks.
Finding API Endpoints for Testing
How to Find API Endpoints for Testing
Identifying API endpoints for testing is a really important step in making sure any application that uses APIs is high-quality, secure, and performs well. This process isn’t just about finding all the accessible API web addresses; it also means understanding what inputs they need (parameters), how you need to log in (authentication requirements), and how they are expected to behave. This thorough approach to discovering endpoints for testing helps cover all possible ways users can interact with the app and uncover any potential weaknesses.
The main and most reliable source for finding endpoints to test is the official API documentation. Good documentation, especially if it follows standards like OpenAPI/Swagger, provides a machine-readable definition of the API. These specifications explain every endpoint in detail: what HTTP methods it supports, what inputs it needs, what format the requests and responses should take, and what error codes it might return. Many APIs host interactive documentation at common URLs like /docs, /api-docs, or /swagger-ui.html. Importing these OpenAPI specifications into testing tools like Postman, SoapUI, or REST Assured can automatically create a complete set of test requests, which dramatically speeds up the test setup process.
Before any testing can begin, it’s absolutely essential to figure out what kind of “authentication” (login) the API endpoints require. This could involve API keys, OAuth tokens, JSON Web Tokens (JWTs), or simple username/password (Basic Authentication). Testers must obtain valid login details for the specific test environment to ensure they can correctly access and interact with the endpoints. It’s also crucial to remember that test environments usually use different main URLs (e.g., https://api-test.example.com instead of https://api.example.com) to keep testing activities separate from the live website, _preventing any accidental impact on real users_.
“API contract testing” is a vital part of checking endpoints. This type of testing confirms that endpoints follow their defined rules, making sure that the request and response formats, status codes, and data types always match what the documentation says. Tools like Dredd, Pact, and Postman’s built-in contract testing features can automatically create tests from API specifications to check endpoint behavior against the agreed-upon “contract.” This helps catch disagreements between the documentation and the actual code early in the development cycle.
Security testing for API endpoints is extremely important. It involves actively searching for common vulnerabilities such as:
- Injection flaws (e.g., SQL injection)
- Broken authentication and authorization
- Excessive data exposure
- Insufficient rate limiting
Tools like Burp Suite and OWASP ZAP are frequently used for these kinds of security assessments. For performance testing, tools like JMeter, Gatling, and k6 can be used to “load test” API endpoints, identifying slowdowns, measuring how quickly they respond under heavy use, and figuring out the maximum amount of traffic the API can handle. By adopting these strategies, teams can ensure that their API endpoints are strong, secure, and performant.
In conclusion, knowing how to find API endpoints is a fundamental skill in today’s interconnected digital world. Whether you’re a developer connecting new services, a security professional protecting applications, or a QA engineer making sure everything works reliably, understanding the various methods and tools for endpoint discovery is incredibly valuable. From watching network traffic in your browser’s developer tools to meticulously analyzing source code, leveraging specialized platforms like Postman, and understanding the architectural patterns of REST APIs, having a diverse toolkit empowers effective exploration. The ongoing challenge of hidden endpoints reminds us of the importance of advanced techniques like fuzzing and mobile application analysis, especially for security. Ultimately, a systematic and comprehensive approach to finding API endpoints not only makes development and integration easier but also plays a crucial role in building more secure and robust web applications.
FAQ
Q1: What is an API endpoint and why is it important to find them?
A1: An API endpoint is a specific web address (URL) that an API uses to access resources and perform operations. It’s like a specific menu item on a server’s menu, acting as a communication point between an application and a server. Finding them is important because it helps developers connect services, allows security researchers to find vulnerabilities, and helps quality assurance (QA) engineers thoroughly test applications.
Q2: How can browser developer tools help in discovering API endpoints?
A2: Browser developer tools, especially the “Network” tab, capture and show all the web requests a page makes in real-time. You can filter these to see just API calls (often labeled XHR/Fetch), inspect all the details of what was sent and received, and even export requests as “cURL” commands to re-test them. As you interact with the website, new API calls appear, giving you a live view of its communication.
Q3: What are some common patterns or keywords to look for when trying to find API endpoints in source code?
A3: When you’re looking at a website’s code, especially JavaScript files, keep an eye out for common URL prefixes like /api/, /v1/, /rest/, or resource-specific paths such as /users. Keywords like “api”, “endpoint”, “fetch”, “axios”, “http”, or the website’s own domain name can help you locate API calls. Also, look for common coding patterns like fetch('URL') or axios.get('URL') that directly show endpoint usage.
Q4: How does Postman assist in the discovery and testing of API endpoints?
A4: Postman offers several helpful features for finding endpoints. The Postman Interceptor Chrome extension can capture your browser’s web traffic and turn it into Postman requests. You can also import official API documentation (like OpenAPI/Swagger files) to automatically create collections of endpoints. Postman also provides “environment variables” for easy testing across different settings and a “Collection Runner” to execute many requests in a sequence.
Q5: Why are hidden API endpoints a concern, and how can they be found?
A5: Hidden API endpoints are undocumented web addresses that are still accessible, often posing security risks or exposing old, forgotten features. They’re a concern because they might lack proper security checks, leading to vulnerabilities where unauthorized users could access sensitive data. These can be found using techniques like “fuzzing” (trying many different web addresses), analyzing mobile applications’ traffic or code, searching public code repositories like GitHub, using advanced Google search queries (“Google dorking”), or examining Certificate Transparency logs.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.