what is api testing in software? 5 Proven Benefits
I remember early in my career, around 2018, when we were launching an e-commerce platform at ‘InnovateTech Solutions’. We’d built a sleek, user-friendly interface that impressed during demos. However, live testing revealed frustrating customer issues: orders failed despite on-screen success messages, and product displays were inconsistent. The problem wasn’t with the interface, but with the unseen communication between our ordering system and the payment gateway, or our product database and the display components. These communications happen via Application Programming Interfaces, or APIs. That experience was my “aha!” moment, showing me exactly why testing these silent workhorses is critical for any software to function correctly.
API testing is a specialized form of software testing that validates Application Programming Interfaces at their core message layer. It operates independently of the user interface (UI), the part of the application you can see and interact with. Its main goal is to ensure APIs meet expectations for functionality, reliability, performance, and security. Unlike traditional testing that often involves clicking buttons on a screen, API testing bypasses the UI. It communicates directly with the application’s underlying logic and data systems. This direct approach helps discover problems much earlier in development, often before they can appear in the UI. Catching bugs early can significantly cut down on fixing time and costs.
Industry trends underscore the growing importance of this validation. Postman’s 2023 State of API Report highlighted that 93% of developers view API quality as critical or very important. Furthermore, 51% of organizations now perform API validation at multiple stages throughout the software development lifecycle, demonstrating widespread adoption. This focus is well-founded; a 2022 study in the Journal of Software Engineering and Applications found that organizations with comprehensive API validation saw a 64% reduction in post-production defects and a 47% decrease in mean time to resolution (MTTR), especially compared to teams relying mainly on UI testing. Personally, I’ve seen how waiting for UI testing to catch API issues can lead to more complex and expensive fixes, making early interface testing a necessity.
This comprehensive approach typically focuses on validating five main areas. First, functionality ensures the API performs its intended tasks and returns correct information. Second, reliability checks that the connection is stable and results are predictable. Third, performance measures response speed and request handling capacity, ensuring efficiency under load. Fourth, security scrutinizes authentication, authorization, and encryption methods to protect sensitive information and prevent unauthorized access. Finally, compliance verifies adherence to industry standards and regulations. This method thoroughly examines an API’s overall strength and resilience.
While beneficial, API validation is also considered challenging. It requires testers to deeply understand how the API works internally, without the visual cues of a graphical user interface (GUI). This often means examining code directly and using specialized tools, demanding a different skill set than UI testing. Despite these challenges, the global API testing market, valued at $682.5 million in 2022, is projected to reach $2.95 billion by 2030. This growth is largely driven by the increasing use of microservices architecture and cloud-native applications, which heavily rely on APIs for internal communication. Validation can be performed at various levels: “unit testing” for individual API components, “integration testing” for how APIs interact with each other and other systems, and “end-to-end testing” for complete business processes driven by APIs. This layered strategy ensures broad coverage and early issue detection across the software ecosystem.
Understanding API and API Testing in Software
What is API in Software Testing?
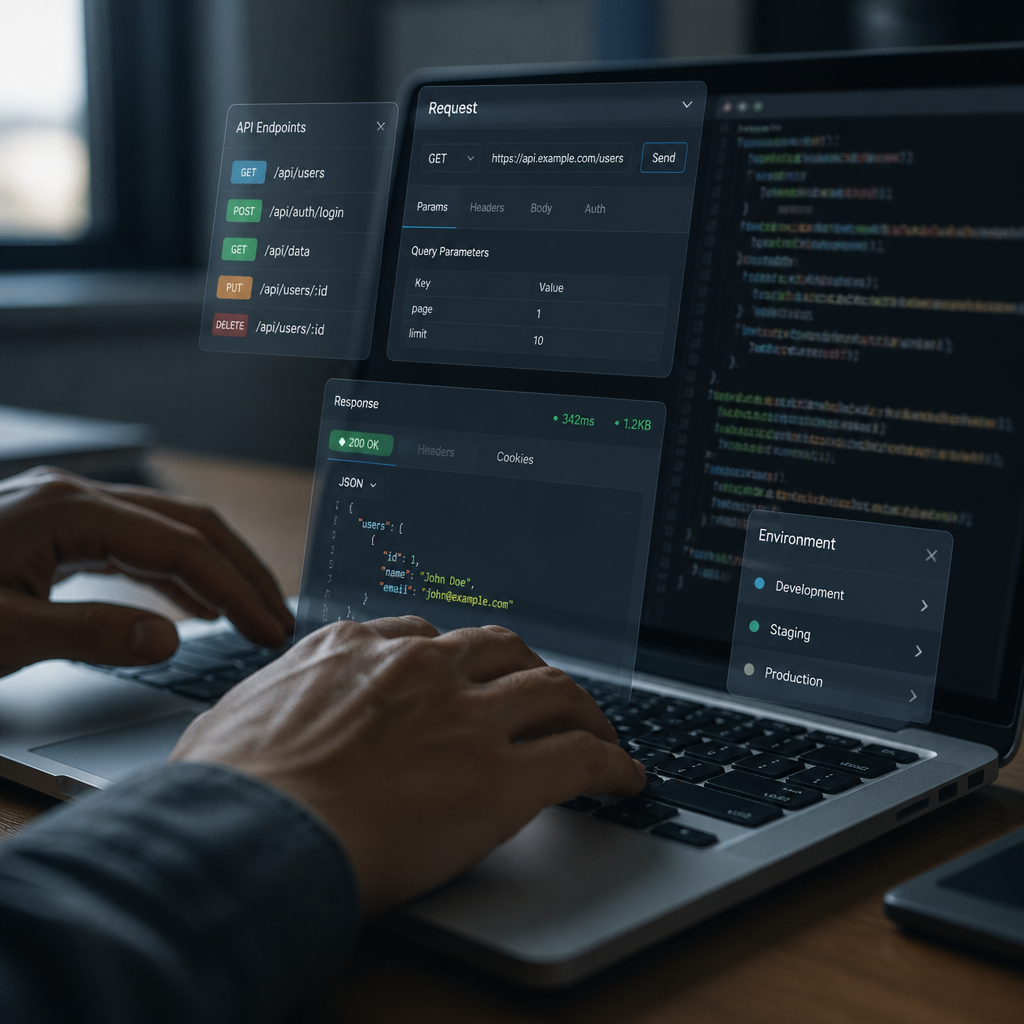
An API, or Application Programming Interface, is a fundamental building block in modern software. Think of it as a set of rules, tools, and definitions that dictate how different software components communicate. In software testing, an API acts as a testable doorway allowing applications or services to exchange information. They send specific requests and receive structured responses, commonly in JSON or XML format, which are simply ways to organize data. These interfaces are crucial because they enable systems to share data and functionality without needing to know the complex internal details of each other. This concept, called “abstraction,” allows a developer to integrate a service, like a payment processor or a map feature, into their app without writing all the underlying code themselves.
APIs employ different architectural styles, each with its own guidelines. REST (Representational State Transfer) is the most popular style, making up about 85% of APIs according to the 2023 Postman State of the API Report. Other important styles include SOAP (Simple Object Access Protocol), GraphQL, and gRPC. As computer scientist Roy Fielding emphasized, the REST style focuses on a “uniform interface” for simplified communication and smoother system interaction.
To truly grasp how APIs function and how to test them, understanding their key components is essential. These include endpoints (specific URLs where API requests are sent), methods (actions like GET, POST, PUT, DELETE), headers (metadata about the request), parameters (data sent with requests), and response codes (numbered status indicators like 200 for success or 404 for not found). Personally, I’ve found that mastering these components is like learning a new language’s grammar; once you understand the verbs, nouns, and nuances, you can effectively communicate with and understand the API.
In software testing, APIs offer valuable interfaces that can be checked independently of the user interface. This capability allows testers to verify underlying business rules, examine data responses for accuracy and format, test error handling, and assess security measures directly at the service level. This approach ensures the application’s core functions are strong and reliable, even before the UI is fully developed. This “shift-left” approach—testing earlier in the development process—helps find and fix issues sooner, preventing more costly repairs later.
Furthermore, API “contracts” establish clear expectations for API behavior. These contracts specify request/response formats, data types, required fields, and expected error messages. They serve as a blueprint against which API tests are written, ensuring a shared understanding between API creators and consumers. Adhering to these contracts is crucial for maintaining compatibility, especially in complex systems. In my experience, sticking to API contracts is vital, particularly with external partners. I recall a project in 2021 at ‘Global Data Connect’ where a minor, unannounced change in a third-party vendor’s API response format caused days of debugging. It highlighted our reliance on these agreements.
Types of API Testing in Software
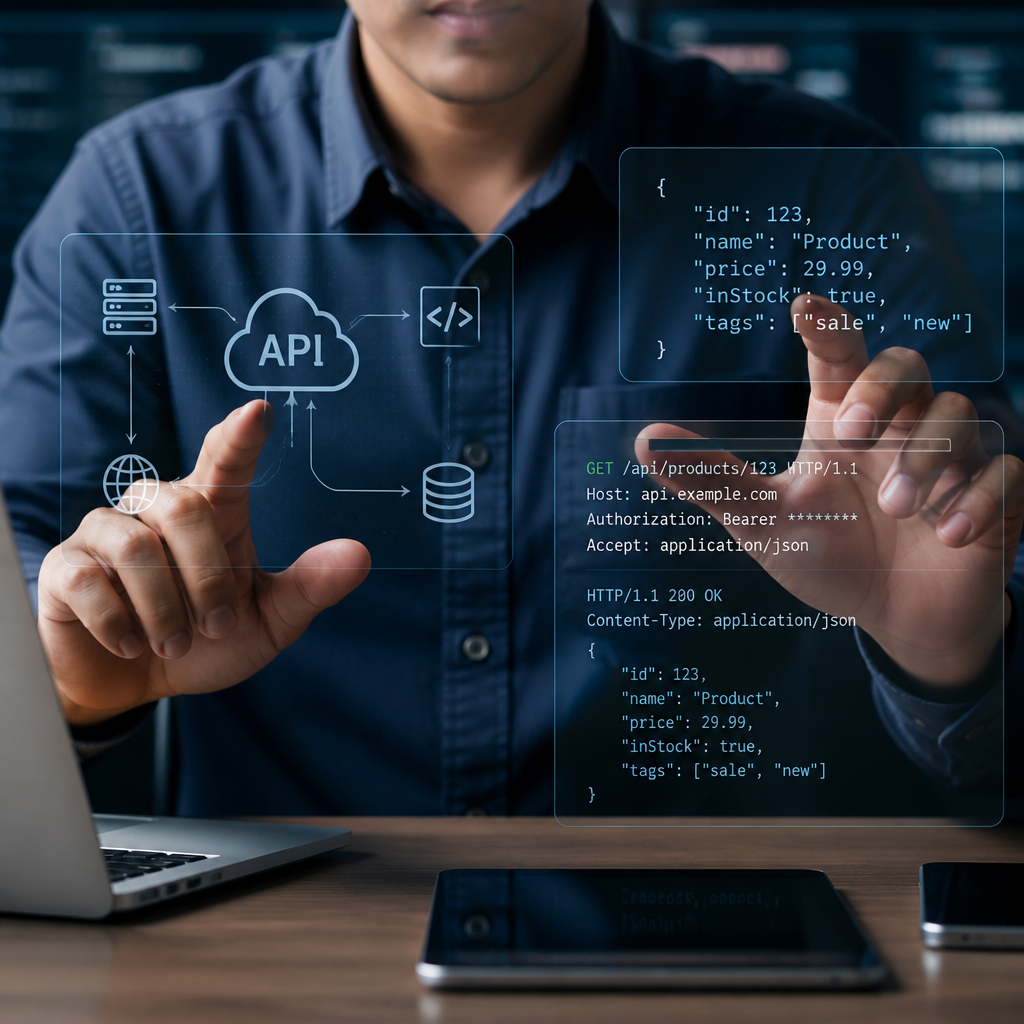
The field of API testing employs various approaches to assess an API’s quality, including its functions, performance, security, and reliability. Each testing type targets specific quality attributes and risk areas, contributing to a comprehensive quality assurance strategy. By combining these testing types, development teams gain a complete understanding of their API’s robustness and readiness for real-world use.
The main types include:
- Functional Testing: This fundamental type confirms that the API behaves precisely as specified. It ensures that given a specific input, the API returns the expected output by checking correct HTTP status codes, response data structure, error handling for invalid inputs, and proper implementation of CRUD (Create, Read, Update, Delete) operations.
- Validation Testing: This type often overlaps with functional testing but specifically focuses on the API’s behavior, data accuracy, and HTTP status code correctness in various scenarios.
- Performance/Load Testing: This assesses the API’s performance under normal and peak usage. It measures response time (latency), throughput (requests per second), and scalability. Industry standards often aim for API response times under 200 milliseconds for optimal user experience.
- Security Testing: This crucial type checks the API for vulnerabilities. It examines authentication, authorization, input validation to prevent attacks like SQL injection, rate limiting, and encryption of sensitive data. According to the 2023 OWASP API Security Top 10, common risks like “broken object level authorization” are top threats. Many teams initially focus only on functional testing, but _neglecting performance or security testing is a common pitfall that often leads to larger problems later_.
- Penetration Testing: This simulates real-world attacks to identify exploitable weaknesses.
- Fuzz Testing: This involves sending large amounts of random or malformed data to an API to test its robustness and uncover potential crashes or security flaws.
- Interoperability Testing: This ensures the API communicates and integrates smoothly with other systems and platforms.
- Contract Testing: Increasingly important in microservices architectures, this verifies that APIs adhere to agreed-upon rules between service providers and consumers, preventing breaking changes.
As the “API Evangelist” Kin Lane emphasizes, a multi-dimensional approach is essential because APIs are the connective tissue of modern applications, and failure in any dimension can cascade across entire systems. This highlights that a comprehensive testing strategy is a necessity for robust applications. Personally, I consider contract testing a game-changer for large microservices architectures, acting as a constantly verified handshake agreement that has saved me countless debugging hours. By systematically applying these testing types, development teams can significantly enhance API quality and stability.
How to Perform API Testing in Software
How to Perform API Testing in Software
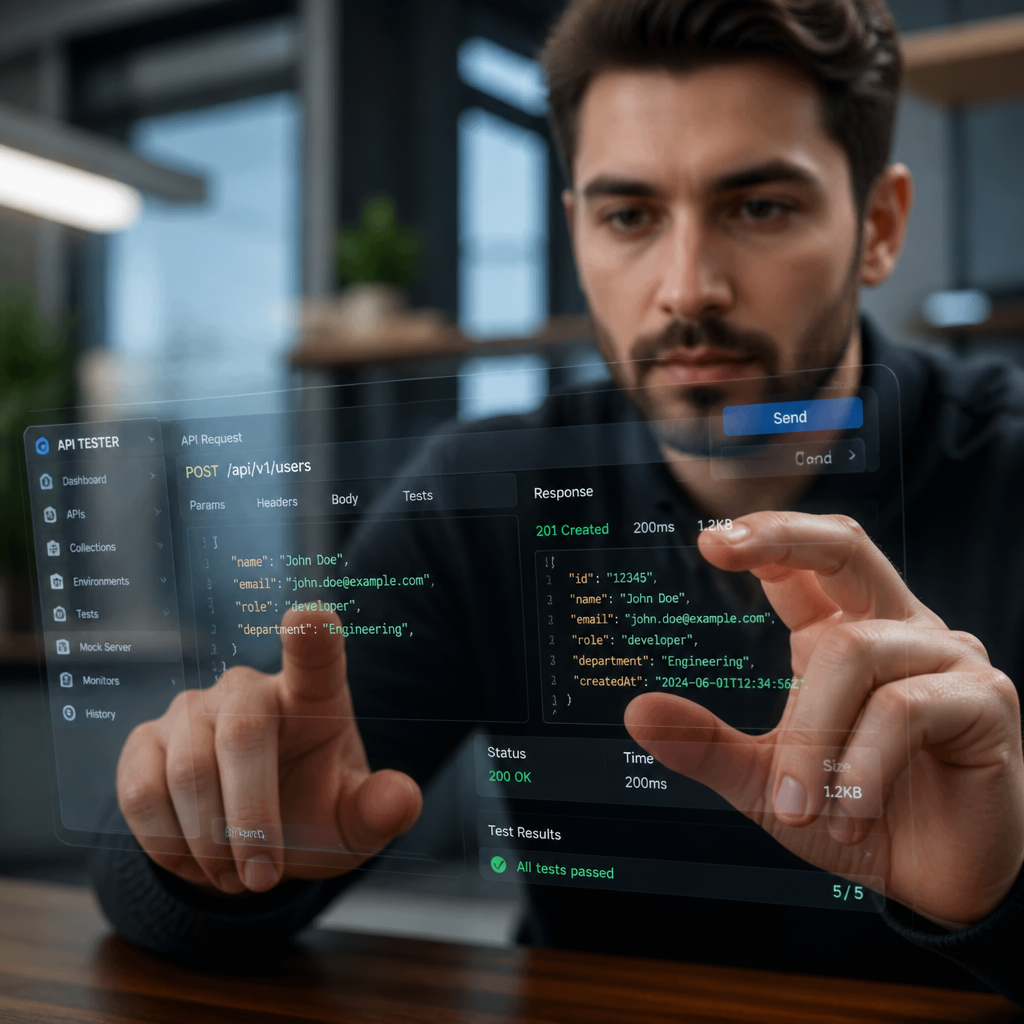
Performing API testing involves a systematic process: sending requests to API endpoints, validating responses against expectations, and confirming the API meets requirements for function, performance, and security. This can be done manually or through automation, with automation being highly recommended for efficiency, especially for “regression testing” and integration into continuous integration (CI) pipelines. The process begins by fully understanding the API’s requirements and documentation. Next, you must set up a suitable test environment that mirrors the live production environment. From there, you define detailed test cases covering positive scenarios (valid inputs), negative scenarios (invalid inputs), and boundary values. The core of the process is executing the API calls using the correct HTTP methods and validating the entire response, including status codes, data, and schema. Finally, use assertions to verify specific conditions and document all results and defects clearly.
Amber Race, Senior Director of Developer Relations at Postman, emphasizes a “shift-left approach where testing begins during API design, not after implementation. Using API specifications like OpenAPI allows teams to generate test cases automatically and catch contract violations before code is written.”
This proactive strategy catches design flaws early, reducing rework costs. I strongly recommend integrating API tests into your Continuous Integration/Continuous Delivery (CI/CD) pipeline. I once worked on a project where manual API tests were run only weekly, delaying critical bug discovery. Automated, nightly runs drastically reduced this time and boosted release confidence. In CI/CD setups, automated API tests run with every code change, providing instant feedback and quickly finding “regressions.” A 2023 study in IEEE Software found that organizations using automated validation in CI/CD pipelines detected 73% of defects before production, a significant improvement over the 41% found by those relying mainly on manual testing.
Good “test data management” is another crucial practice. This involves using separate databases for testing, cleaning data after tests (“teardown”), and creating reusable test data sets. These practices ensure tests are reliable, repeatable, and don’t interfere with other tests or environments. By following this systematic approach, teams build trust in their APIs and the applications they power.
API Testing Tools in Software Development
API testing tools are specialized software applications designed to streamline and enhance the validation process. They assist with creating requests, validating responses, automating tests, and integrating into broader development workflows. These tools offer features that simplify the complex task of interacting directly with APIs, making the process more accessible and efficient for both developers and QA engineers. The market offers a variety of leading options. Postman is a globally popular GUI-based platform known for its ease of use, collaboration features, and robust automation capabilities. For enterprise SOAP services, SoapUI provides comprehensive features for functional, security, and load testing. For teams who prefer writing tests in code, REST Assured is a powerful Java library with a readable domain-specific language (DSL).
Other popular tools include Katalon Studio, a comprehensive codeless automation platform; Apache JMeter, an open-source tool primarily used for performance and load testing; and Insomnia, a lightweight and user-friendly REST client for quick manual testing. An innovative option is Karate DSL, an open-source framework that combines testing, mocks, and performance evaluation into a single, readable language. Even documentation tools like Swagger/OpenAPI can aid testing by allowing users to interact with endpoints directly from the documentation. The 2023 Postman State of the API Report indicates that 89% of developers use specialized API validation tools, with Postman, Swagger/OpenAPI, and JMeter being the most common. As Angie Jones, Senior Director of Developer Relations at TBD, advises, the best tool depends on your team’s technical skills and workflow.
API Testing Best Practices in Software
Adopting best practices for this process ensures the testing is thorough, efficient, and maintainable, leading to higher software quality. These proven methods cover test design, automation, security, performance, and integration into daily development. Following these practices maximizes the value of validation efforts and builds more robust applications.
Fundamental best practices include:
- Test Early in the Development Cycle (Shift-Left Testing): Begin testing APIs as soon as they are designed, even before full implementation. This proactive approach helps catch design flaws and “contract violations” early, significantly reducing bug-fixing costs.
- Organize Tests by Functionality and Priority: Structure test suites logically, grouping tests by API endpoint or business function, and prioritize critical paths first.
- Use Positive and Negative Test Cases: Design tests for both expected behavior (“positive testing”) and error handling with invalid inputs (“negative testing”).
- Implement Data-Driven Testing: Use external data sources to run the same test logic with various input data sets, which efficiently covers a wide range of scenarios.
- Validate Both Success and Error Responses: Beyond checking for a 200 OK status, thoroughly examine the content and structure of successful responses and verify that error responses provide clear messages and correct HTTP status codes.
- Test Security and Authentication Thoroughly: Rigorously test all authentication mechanisms, authorization rules, and common vulnerabilities. Ensure HTTPS is enforced and test rate limiting. _Never hardcode credentials like passwords or API keys directly into test scripts_; always use environment variables.
- Automate Regression Tests: Once tests are stable, automate them to ensure new code changes don’t break existing functionalities.
- Integrate Tests into CI/CD Pipelines: Embed automated API tests into the CI/CD pipeline so they run automatically with every code change, providing immediate feedback.
- Monitor API Performance: Continuously track API response times, request handling capacity, and error rates, especially in live production environments.
- Maintain Clear Test Documentation: Document test coverage and keep API specifications (e.g., OpenAPI/Swagger) up-to-date, as they serve as the official “contract” for API behavior.
By diligently applying these best practices, teams can build highly reliable, secure, and performant APIs that form the robust foundation of modern software applications.
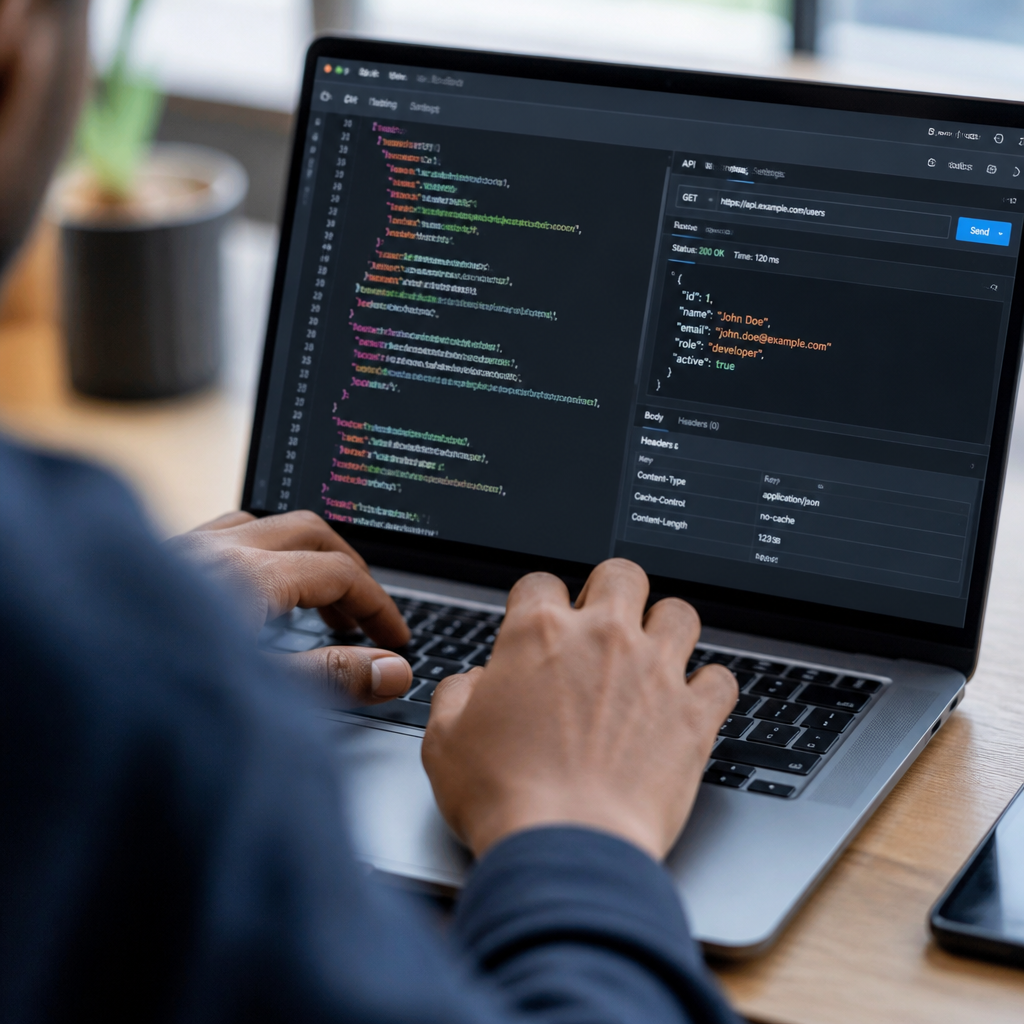
API Testing Compared to Other Testing Approaches
API Testing vs Unit Testing in Software
In software quality assurance, both API testing and “unit testing” are important but operate at different levels of the “testing pyramid,” serving distinct scopes and purposes. API testing primarily checks the function, reliability, performance, and security of Application Programming Interfaces at the “service” or “integration” layer. It focuses on the API’s external behavior—how it responds to requests and interacts with other system parts. In contrast, unit testing verifies individual, smallest code units, such as functions, methods, or classes, by testing them in isolation. It dives into the internal logic of these tiny application pieces, ensuring they work correctly on their own.
| Feature | Unit Testing | API Testing |
|---|---|---|
| Scope | Narrowest: individual functions or methods. | Broader: entire API endpoints and business logic flow. |
| Granularity | White-box: requires source code access. | Black-box: interacts with the public interface. |
| Dependencies | Isolated, using mocks or stubs. | Involves real dependencies like databases and other services. |
| Speed | Extremely fast (milliseconds). | Slower (seconds to minutes) due to network calls. |
Unit testing is usually performed by developers during coding, using frameworks like JUnit or pytest. These tests run quickly, offering immediate feedback. This method can be done by both developers and quality assurance (QA) engineers, as it doesn’t require source code access. Personally, I find unit tests invaluable for quickly verifying code’s “nuts and bolts,” while API tests give me confidence that those parts are correctly assembled and communicating.
Martin Fowler, Chief Scientist at ThoughtWorks, explains the complementary roles of these tests through the “testing pyramid” principle: “The testing pyramid suggests you should have many more unit tests than API/service tests, and more API tests than UI tests. Unit tests are fast and pinpoint failures precisely, while API tests validate integration points and business workflows. Both are essential—unit tests catch logic errors early, API tests catch integration issues.”
According to this principle, a healthy test suite ideally comprises approximately 70% unit tests, 20% integration/API tests, and 10% end-to-end/UI tests. While the testing pyramid is widely accepted, some practitioners advocate for a “testing trophy” model, suggesting that integration tests provide better confidence and are less fragile than _unit tests heavily reliant on simulated components_. Ultimately, the best practice is to use both unit and API validation together: unit tests for detailed logic within functions, and interface tests for validating service contracts, data storage, and component interactions. This combined approach ensures the most comprehensive quality coverage.
—
In conclusion, API testing is a foundational practice in modern software development, essential for building robust, reliable, and secure applications. By directly interacting with the application’s core logic at the message layer, it enables early defect detection, ensures seamless integration between components, and validates critical aspects like performance and security. While challenging, the significant benefits—including reduced defect rates and faster resolution times—make it an indispensable part of the software development lifecycle. As applications continue to evolve with microservices and cloud-native architectures, the strategic implementation of API testing, supported by appropriate tools and best practices, will remain paramount for delivering high-quality software that truly meets user expectations and business demands.
FAQ
Q1: What is the primary difference between API testing and UI testing?
A1: The primary difference lies in the layer of the application being tested. API testing validates the application’s underlying business logic and data layer directly at the message level, bypassing the user interface (UI). UI testing, on the other hand, interacts with the application through its graphical user interface, simulating user actions to verify visual elements and complete end-to-end user journeys. API testing is generally faster and helps catch bugs earlier, while UI testing confirms the actual user experience.
Q2: Why is API testing considered challenging?
A2: API testing is considered challenging because it requires testers to understand the API’s functionality and expected behavior without the visual cues of a graphical user interface (GUI). This often necessitates direct interaction with the codebase, a deep understanding of API specifications (the rules and descriptions for the API), and the use of specialized testing tools, demanding a different skill set than traditional UI testing.
Q3: What are the key aspects validated during API testing?
A3: API testing typically validates five key aspects: functionality (does the API work as expected?), reliability (consistent connection and results), performance (response time and how many requests it can handle), security (authentication, authorization, and encryption), and compliance (adherence to industry standards and regulations).
Q4: Can API testing be automated, and what are the benefits of automation?
A4: Yes, API testing can be highly automated using various tools and frameworks like Postman, REST Assured, or SoapUI. The benefits of automation include faster execution of tests, improved efficiency, the ability to run tests frequently (e.g., in CI/CD pipelines) for quick feedback on code changes, reduced manual effort, and better coverage for regression testing (checking that new changes haven’t broken old features).
Q5: How does API testing fit into the “testing pyramid” concept?
A5: In the testing pyramid, API testing (often categorized as integration or service testing) sits above unit testing and below UI testing. This model suggests having many fast, isolated unit tests, a moderate number of API tests to validate how different parts integrate and how business processes work, and a smaller number of slower, end-to-end UI tests. This balance provides faster feedback, easier debugging, and more stable test suites.

Hi, I’m Anna Smith, the founder of API Dev Note.
I’m an API specialist with experience working with APIs, integrations, and web development. Through hands-on projects, I’ve learned that understanding how APIs work in real-world environments is just as important as reading the documentation.